 By admin
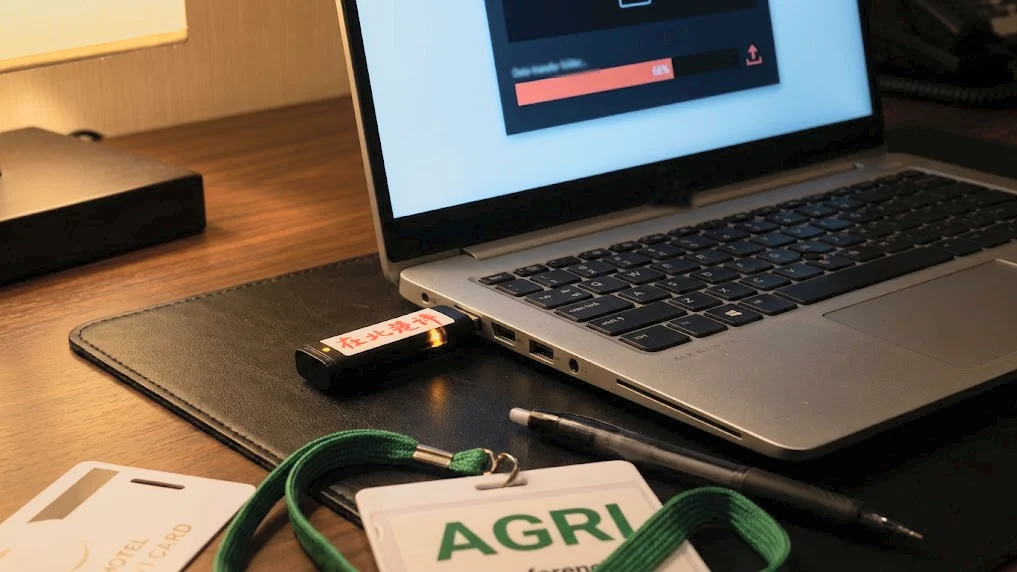
In a sophisticated and unsettling display of state-sponsored cyber espionage, a Chinese hacking group, identified by CrowdStrike as OVERCAST PANDA, successfully infiltrated executive laptops at an agricultural industry conference held on the tropical island of Hainan this spring. The breach, detailed in CrowdStrike’s comprehensive 2026 Threat Hunting Report, bypassed conventional cybersecurity defenses such as phishing emails and network intrusions. Instead, the adversaries meticulously gained physical access to hotel rooms, compromising devices by booting them from a USB stick while their unsuspecting owners were attending evening events. This audacious "evil maid" attack highlights a concerning evolution in cyber warfare, leveraging physical access as a primary vector for malware deployment.
CrowdStrike’s analysis, corroborated by interviews with Adam Meyers, Senior Vice President of Counter Adversary Operations, reveals a precise timeline for the intrusions. The report indicates that between March and May 2026, intruders entered hotel rooms occupied by conference attendees. One entry was recorded around 8 p.m. local time, with a second room breached by 9:57 p.m. During these brief windows of opportunity, the attackers installed a sophisticated backdoor known as FlowCloud directly onto the laptops’ storage devices. Following the malware installation, the machines were rebooted, leaving no trace of a network intrusion, phishing attempt, or compromised credentials through traditional login methods.
The FlowCloud malware itself is not new, having been documented by Proofpoint in 2020 as part of attacks targeting the U.S. utilities sector via phishing campaigns. More recently, NTT Security’s Security Operations Center (SOC) has tracked USB-delivered infections by this malware at overseas branches of Japanese organizations since early 2022, underscoring its persistent and adaptable nature. However, the method employed by OVERCAST PANDA represents a significant escalation. Security researchers have long recognized the "evil maid attack," a term popularized by Joanna Rutkowska in 2009, where an attacker with physical access to an unattended laptop can tamper with it, often using a bootable USB. While physical access operations are relatively rare among the 290 named adversaries tracked by CrowdStrike, OVERCAST PANDA’s approach is novel. Unlike the MUSTANG PANDA group, which relies on victims inadvertently plugging in a dropped USB drive, OVERCAST PANDA’s operation involved direct physical entry into hotel rooms by state intelligence operatives. This combination of state intelligence service involvement and direct malware deployment via a bootable USB, circumventing user interaction for execution, marks a critical development in threat actor methodologies.
Upon powering on their devices the following morning, the targeted executives unknowingly triggered FlowCloud. The malware then commenced its covert operations, including keylogging, screen capture, file collection, and credential harvesting. Meyers explained to VentureBeat that CrowdStrike’s visibility into these operations begins once the operating system loads and the FlowCloud implant activates. A registry key or similar trigger initiates FlowCloud’s execution sometime after the OS boots, at which point CrowdStrike’s Falcon sensor can detect its presence. The critical vulnerability lies in the temporal gap between the USB write operation and the subsequent boot-up, a period during which the laptop remains compromised and undetected by conventional endpoint security solutions.
CrowdStrike disclosed this campaign just a month before unveiling its new suite of AI security products at Fal.Con 2026. These include Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway, all designed to address emerging threats, including those that bypass traditional defenses.
Why Existing Security Tools Missed the Mark
The effectiveness of OVERCAST PANDA’s attack lies in its ability to circumvent multiple layers of standard security. Endpoint Detection and Response (EDR) solutions require the operating system to be loaded and their agents to be running. Multi-factor authentication (MFA) typically waits for a login attempt, phishing training addresses malicious emails, and AI agent security focuses on securing agents once they are active. OVERCAST PANDA’s physical access vector completely bypasses these security controls at the point of entry. The initial compromise occurred below the running operating system, beneath the EDR agent, and outside the authentication stack. While Falcon successfully detected FlowCloud once its process began after the boot, the implant and its trigger mechanism were already deeply embedded on the laptop’s disk.
"Hotel entry is a very common thing," Meyers observed, noting that corporate physical security professionals are generally aware of such risks. "But I think what is unique is the combination of hotel entry with deployment of malware." Meyers posits that China’s Ministry of State Security (MSS) likely orchestrates OVERCAST PANDA’s activities. The individuals gaining physical access could be MSS or Ministry of Public Security officers, or compromised or coerced hotel housekeeping staff. The report also details a separate mid-2026 intrusion targeting a U.S.-based media professional employing identical tradecraft. The specific targeting of an agricultural conference aligns with intelligence collection priorities linked to China’s strategic five-year plans, suggesting a focus on technology transfer, resource acquisition, or policy influencing within the global agricultural sector.
CrowdStrike’s Fal.Con Announcements and the Dawn of Runtime Security
At Fal.Con 2026, CrowdStrike showcased significant advancements in AI-driven security. Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to unveil SafeMind, an agentic cybersecurity system built upon Nvidia’s Nemotron open models and CrowdStrike’s extensive threat intelligence. Meyers highlighted the escalating threat landscape, stating that 7,400 Common Vulnerabilities and Exposures (CVEs) were registered in June 2026, a staggering 96% increase over June 2025. CrowdStrike itself was responsible for the responsible disclosure of approximately 2,400 of these CVEs, representing roughly 30% of all registered vulnerabilities that month.
Falcon Guardian, CrowdStrike’s runtime security solution for AI agents on endpoints, was officially launched during the conference. AI Gateway, a component of Guardian, is slated for a September release as a hosted service, with a hybrid version to follow. AJ Shipley, CrowdStrike’s Chief Product Officer, indicated that SafeMind models will be integrated into Guardian within weeks, enabling malicious prompt detection.
These new products are designed to combat a range of escalating threats. The report quantifies this surge, noting that AI agent-triggered detection leads grew at 2.5 times the rate of human-triggered leads, according to CrowdStrike’s OverWatch team. Cloud-conscious eCrime activity saw a substantial 171% increase during the reporting period. Vishing intrusions doubled in the first half of 2026 compared to the latter half of 2025, with the eCrime group SNARKY SPIDER demonstrating alarming efficiency by moving from account takeover to data exfiltration in under five minutes after compromising Single Sign-On (SSO)-integrated SaaS applications. Crucially, all these network-based threats assume a running operating system, an active user session, or a live cloud workload – vulnerabilities that OVERCAST PANDA’s physical attack bypasses.
The Unsung Heroes: Firmware and Policy Controls
Meyers asserts that the solution to such physical-access attacks is attainable, albeit often inconvenient. "It’s a solvable problem," he stated, "It’s just an inconvenient solution, which means that a lot of people don’t do it." CrowdStrike has, for years, offered firmware attack detection and BIOS settings auditing capabilities through its Falcon sensor, including integration with Dell SafeBIOS since May 2019. This functionality, allowing for the auditing of security-related BIOS settings on executive laptops, has been available for seven years, implying that its non-deployment for travel devices is a policy decision rather than a product gap.
The controls that could have effectively mitigated the OVERCAST PANDA campaign are fundamental and cost-effective. Disabling external boot in Unified Extensible Firmware Interface (UEFI) settings is paramount. A BIOS administrator password is essential to maintain this disabled state. Pre-boot authentication ensures that even if a foreign boot environment is loaded, the encrypted volume remains inaccessible until a human provides a PIN or cryptographic key. Furthermore, firmware monitoring can detect tampering after the fact.
Meyers offered stark advice: "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He personally utilized temporary laptops and disposable email accounts for overseas travel while at CrowdStrike, meticulously wiping devices upon return. He also pointed out that the exposure begins at customs, where officials can seize devices and compel logins. Even seemingly secure hotel safes are not foolproof, as he described them as having "master keys."
The Tyranny of Scale: Why Network Threats Dominate Security Budgets
Intrusion attempts tracked by CrowdStrike OverWatch have shown a consistent rise, growing approximately 4% during the reporting period after a 27% surge the previous year. CrowdStrike attributes this plateau to a strategic shift by threat actors towards more complex and resource-intensive campaigns, exemplified by the OVERCAST PANDA hotel room operation.
Despite the ingenuity of the physical attack, Meyers expressed greater concern about network-based threats. When asked to compare OVERCAST PANDA’s hotel room campaign with the REVENANT SPIDER case, an eCrime group that utilized AI to compromise 17 victims with custom web shells in just 48 minutes, Meyers favored REVENANT SPIDER as the more significant threat. His reasoning is rooted in scalability: "You can’t intrude on hotel rooms at scale. You can’t intrude on physical devices at scale. And even then, it’s just one device." Physical-access tradecraft is inherently limited by geography and the number of available targets. In contrast, network-speed, AI-powered intrusions can affect a vast number of machines simultaneously. Consequently, security budgets tend to follow the threat that impacts the greatest number of assets, leaving less attention and funding for the harder-to-detect, albeit less scalable, physical attack vectors.
However, for the executives attending the agricultural conference, the state intelligence service’s deliberate choice of a slow, unscalable method was precisely because it succeeded where network-based attacks would have failed. The conference itself, therefore, becomes the primary threat model, with its attendees serving as high-value targets.
The Conference as a Threat Model: Bridging the Organizational Divide
The executives attending conferences represent the direct targets of such campaigns, and as established, runtime security only begins once a machine boots. Ironically, the vendors exhibiting at Fal.Con 2026 were showcasing the very runtime protection solutions that attendees might need for their own laptops, which harbor the same inherent vulnerabilities. The fundamental challenge lies in organizational fracture. Falcon Guardian might be managed by one team, while BIOS configuration on travel laptops falls under another. The Agentic Identity Provider could be deployed by identity governance, while the decision of whether executives carry production-access machines to international conferences might rest with yet another department. Budget allocations for cloud threat defense are often entirely separate from travel device policies. Meyers, having experienced both sides of this issue, noted the disconnect: "I’ve talked to companies where they’re like, we’re having a board meeting in Shanghai, and I’m like, why would you do that?"
Essential Pre-Trip Security Measures for Leaders
For security leaders preparing for international travel, a critical audit of executive laptops is imperative. The immediate priority is to verify the USB boot status of every device. If a laptop can currently boot from a USB drive, it possesses the same exploitable gap that OVERCAST PANDA leveraged. For Windows laptops, the primary target of FlowCloud, several essential steps are recommended:
Enforce full-disk encryption coupled with pre-boot authentication. BitLocker configured with TPM-only protection is a known vulnerability against physical access attacks. Researchers have demonstrated the ability to extract the volume master key from the LPC bus with inexpensive hardware, and similar exploits over SPI have been documented. OVERCAST PANDA’s ability to write a backdoor and its post-boot trigger to the Windows volume suggests either unencrypted devices or configurations that were circumvented. Pre-boot authentication using a PIN or a USB key introduces a mandatory human step before storage becomes accessible, significantly mitigating this risk.
Verify that Secure Boot is enabled and the revocation list is up-to-date. Secure Boot validates the signatures of boot components, blocking most unauthorized bootloaders. However, it does not prevent booting from external media, and signed shims can still contain bypasses. ESET research has highlighted legacy Microsoft-signed UEFI shims that allowed untrusted code to run at boot, undermining Secure Boot. While Microsoft has since revoked these shims, laptops that have not received the latest updates remain vulnerable. To further strengthen defenses, the boot order should be locked at the UEFI level, one-time boot menus disabled, and a BIOS administrator password implemented to protect both the setup utility and any boot override keys. Meyers’ assessment is that many organizations neglect these settings due to the perceived inconvenience of implementation.
Finally, issue dedicated travel-only devices for international conferences. These devices should have no access to production systems, no saved credentials for internal tools, and no persistent VPN configurations. As Meyers pithily stated, citing an old DEF CON adage, "If they can get their hands on it, they can own it." Falcon catches FlowCloud only after boot, leaving a critical window of exposure during the hours between the USB write and the next login, while the compromised laptop sits closed.
Meyers concluded with practical advice: "It’s cheap to buy a couple of laptops and a couple of phones." The controls that effectively close the gap exploited by OVERCAST PANDA are a handful of firmware settings and a dedicated travel device. The pertinent question remains whether organizations are willing to implement these measures before their executives become the next targets.
