
 By admin
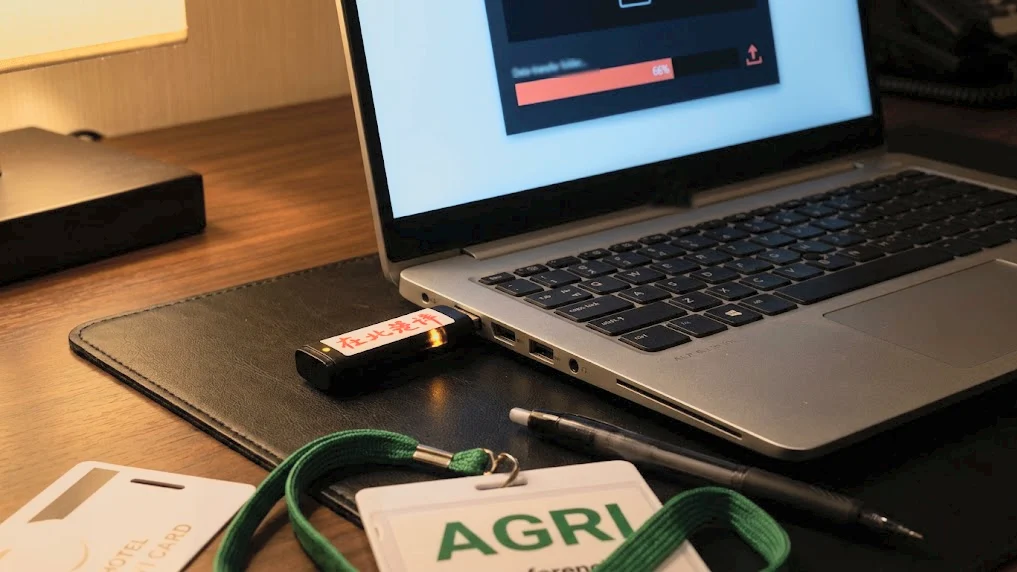
A sophisticated and audacious cyberattack campaign orchestrated by a Chinese state-linked hacking group, tracked by cybersecurity firm CrowdStrike as OVERCAST PANDA, has come to light, revealing a chillingly effective tactic that bypasses conventional digital security measures. This operation, detailed in CrowdStrike’s 2026 Threat Hunting Report, involved compromising executive laptops at an agricultural industry conference on Hainan Island during the spring of 2026. Instead of resorting to the more common methods of phishing or network breaches, the attackers physically infiltrated hotel rooms to install malware directly onto devices while their targets were away, a method colloquially known as an "evil maid attack."
The intrusion timeline, meticulously pieced together by CrowdStrike’s OverWatch team and shared in an interview with VentureBeat at Fal.Con 2026, paints a picture of stealth and precision. The operation commenced with an intruder entering one executive’s hotel room around 8 p.m. local time, followed by a second room by 9:57 p.m. During these brief windows of opportunity, the attackers directly wrote a sophisticated backdoor, dubbed FlowCloud, onto each laptop’s storage. The machines were then re-booted and left as they were, with no trace of network intrusion, no phishing emails sent, and no credentials stolen through deceptive login pages. The effectiveness of this method lies in its complete circumvention of typical endpoint detection and response (EDR) systems, multi-factor authentication (MFA), and user awareness training, all of which rely on the operating system being active or user interaction.
The CrowdStrike report dates these specific intrusions to between March and May 2026. Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, confirmed these timestamps in the VentureBeat interview, emphasizing the novel combination of physical access with direct malware deployment. While the FlowCloud backdoor itself is not new, having been documented by Proofpoint in 2020 delivered via phishing to the U.S. utilities sector, and NTT Security tracking USB-delivered infections since early 2022, its application in this physical-access scenario marks a significant escalation.
The concept of an "evil maid attack" dates back to 2009 when Joanna Rutkowska demonstrated a similar technique using a bootable USB stick to compromise systems protected by TrueCrypt. However, such physical-access operations are exceptionally rare among the 290 named adversaries tracked by CrowdStrike. While other groups, such as MUSTANG PANDA, have employed methods involving victims plugging in a dropped USB stick, OVERCAST PANDA’s approach is distinguished by the direct, unassisted boot-from-USB installation of malware by a state intelligence service, bypassing the need for any user interaction post-infection.
Upon powering on their laptops the following morning, the compromised executives inadvertently triggered the malware. FlowCloud then silently loaded, initiating a suite of malicious activities including keylogging, screen capture, file collection, and credential harvesting. "We have the visibility once the machine boots up," Meyers explained to VentureBeat, noting that a registry key or similar trigger activates FlowCloud shortly after the operating system loads. This is precisely when CrowdStrike’s Falcon sensor can detect its presence. The critical vulnerability, however, lies in the period between the USB write and the subsequent boot – hours during which the laptop remains compromised and undetected before the executive logs back in.
This revelation from CrowdStrike comes strategically a month before the company announced its new slate of AI security products at Fal.Con 2026: Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway. These advanced solutions aim to address evolving threats, but the OVERCAST PANDA campaign highlights a fundamental gap that predates many AI-driven security advancements.
Why Existing Security Tools Failed to Detect the Initial Compromise
The success of the OVERCAST PANDA campaign underscores a critical failing of many contemporary security tools. Endpoint Detection and Response (EDR) solutions, for instance, require the operating system to be loaded and their agents to be running to function effectively. Multi-factor authentication (MFA) solutions are designed to protect against unauthorized logins, and phishing training aims to educate users about malicious emails. AI agent security, while promising, typically focuses on securing agents that are already operating within the system. OVERCAST PANDA bypassed all of these by compromising the machine at a level below the running OS, below the EDR agent, and below the authentication stack. While Falcon eventually detected FlowCloud once its process began after booting, the implant and its trigger mechanism were already firmly entrenched on the disk.
"Hotel entry is a very common thing," Meyers observed, drawing a parallel to concerns voiced by corporate physical security professionals. "I think what is unique is the combination of hotel entry with deployment of malware." He posits that China’s Ministry of State Security (MSS) is likely behind OVERCAST PANDA, with the individuals entering the rooms being either MSS officers, Ministry of Public Security agents, or potentially bribed or coerced hotel housekeeping staff. The report also indicates that a similar intrusion targeting a U.S.-based media professional occurred in mid-2026, employing the same sophisticated tradecraft. The specific targeting of an agricultural conference aligns with intelligence collection priorities that Meyers has previously linked to China’s strategic five-year plans.
CrowdStrike’s Fal.Con Announcements and the Dawn of Runtime Security
The unveiling of CrowdStrike’s AI security product suite at Fal.Con 2026, including an appearance by Nvidia CEO Jensen Huang to discuss SafeMind, a collaborative agentic cybersecurity system built on Nvidia Nemotron open models and CrowdStrike’s threat intelligence, signals a proactive response to these emerging threats. Meyers highlighted the alarming growth in vulnerabilities, noting that 7,400 CVEs were registered in June 2026, a staggering 96% increase over June 2025, with CrowdStrike responsible for submitting approximately 30% of these through responsible disclosure.
Falcon Guardian, designed as a runtime security layer for AI agents on endpoints, was made available immediately at the conference. AI Gateway, initially presented as a capability within Guardian, is slated for a September release as a hosted service, with a hybrid version to follow. AJ Shipley, CrowdStrike’s chief product officer, confirmed that a SafeMind model will be integrated into Guardian within weeks, enhancing its ability to detect malicious prompts.
These new products are poised to address a growing landscape of threats, as quantified by CrowdStrike’s report. AI agent-triggered detection leads have outpaced human-triggered leads by 2.5 times, according to OverWatch. Cloud-conscious eCrime activity has surged by an alarming 171% during the reporting period. Furthermore, vishing intrusions have doubled in the first half of 2026 compared to the latter half of 2025, with the eCrime group SNARKY SPIDER demonstrating a concerning acceleration, moving from account takeover to data exfiltration in under five minutes after compromising SSO-integrated SaaS applications. Significantly, all these threats are network-based and rely on a running OS, active user sessions, or live cloud workloads – precisely the layers OVERCAST PANDA’s physical intrusion circumvented.
Firmware and Policy: The Unsung Heroes of Physical Security
Despite the sophistication of the OVERCAST PANDA attack, Meyers asserts that the problem is "solvable," albeit through inconvenient means. The controls that could have effectively blunted this campaign are not new or complex; rather, they are foundational and often overlooked. CrowdStrike itself has offered firmware attack detection and BIOS settings auditing capabilities through its Falcon sensor since May 2019, including a Dell SafeBIOS integration that surfaces BIOS verification telemetry within the Falcon console. The ability to audit security-related BIOS settings on travel laptops has been present within the platform for seven years, making its non-implementation a matter of organizational policy and decision-making rather than a product gap.
The core controls that would have mitigated the OVERCAST PANDA campaign are remarkably straightforward: disabling external boot in UEFI firmware removes the primary attack vector. Implementing a BIOS administrator password prevents unauthorized changes to these critical settings. Pre-boot authentication, requiring a PIN or USB key before the operating system loads, ensures that even if a foreign boot environment is introduced, the encrypted data remains inaccessible. Finally, firmware monitoring can detect tampering after the fact.
"Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service," Meyers advised, echoing a sentiment of extreme caution for travelers. He personally adopted the practice of using temporary laptops and disposable email accounts for overseas trips, wiping devices upon return. The exposure, he notes, can begin as early as customs, where officials have the authority to seize devices and compel logins. Even hotel safes offer little solace, as Meyers wryly observed, "They have master keys to that stuff."
The Tyranny of Scale and the Neglected Threat
CrowdStrike’s OverWatch team observed a roughly 4% increase in tracked intrusions over the reporting period, following a substantial 27% rise the previous year. This plateau is attributed by CrowdStrike to a strategic shift towards more complex and resource-intensive campaigns, exemplified by the OVERCAST PANDA hotel room operation. When asked to compare this physical intrusion to the REVENANT SPIDER campaign – an eCrime group that utilized AI to compromise 17 victims with custom web shells in a mere 48 minutes – Meyers identified REVENANT SPIDER as the more concerning threat to the average enterprise.
"You can’t intrude on hotel rooms at scale," Meyers stated. "You can’t intrude on physical devices at scale. And even then, it’s just one device." Physical-access tradecraft, while effective against specific, high-value targets, is inherently unscalable. In contrast, network-speed, AI-powered intrusions can affect a vast number of machines simultaneously. Security budgets, driven by the need to address the most widespread threats, naturally gravitate towards these scalable attacks. This leaves the less scalable, but equally insidious, physical intrusion methods to exploit the vulnerabilities that remain unaddressed due to their perceived limited reach.
However, the executives who attended the agricultural conference in China this spring were precisely the meticulously selected targets of a state intelligence service that deliberately chose a slow, unscalable method precisely because it succeeds where network-based attacks are rendered impotent. The conference itself, with its concentration of high-value targets in a controlled environment, served as the ideal operational theater for such a tactic.
The Conference as a Threat Model and the Fractured Security Landscape
The executives attending such conferences represent the prime targets for this type of campaign, and the critical window of vulnerability exists from the moment the machine is compromised until it is next booted. The vendors exhibiting at Fal.Con 2026, showcasing a wide array of security solutions, were largely promoting runtime protection for AI agents and endpoints, technologies that become relevant only after the operating system has loaded – the very point that OVERCAST PANDA’s attack bypasses.
The true organizational challenge lies in the fragmentation of security responsibilities. Falcon Guardian might be deployed by one team, while the crucial BIOS configuration for travel laptops falls under the purview of another. The Agentic Identity Provider might be rolled out by identity governance, while the decision of whether executives carry production-access machines to international conferences rests with yet another department. Furthermore, the budget allocated for cloud threat defense often bears no relation to the policies governing travel device security. Meyers, having experienced both sides of this divide, has encountered companies making demonstrably risky decisions, such as holding board meetings in potentially insecure locations like Shanghai without adequate security precautions.
Essential Pre-Trip Security Measures for Leaders
To preemptively address the vulnerabilities exploited by OVERCAST PANDA, security leaders must undertake a thorough audit of every executive laptop, specifically focusing on USB boot capabilities. If a device can be booted from USB in its current state, it possesses the same critical gap that the group exploited. The following steps, applicable to Windows laptops which FlowCloud targets, are essential for closing this window of exposure:
Firstly, enforce full-disk encryption coupled with robust pre-boot authentication. While BitLocker, when configured with TPM-only, offers a baseline of protection, it has been identified as a potential weak point against sophisticated physical access attacks. Researchers from SCRT demonstrated in 2021 how the volume master key could be extracted from the LPC bus using a low-cost FPGA module. Similarly, Dolos Group achieved the same over SPI the same year. OVERCAST PANDA’s ability to write a backdoor and its post-boot trigger directly to the Windows volume implies that the targeted machines were either unencrypted or protected by a configuration that the attackers could circumvent. Pre-boot authentication, requiring a PIN or USB key, introduces a crucial human verification step before the encrypted storage becomes accessible, effectively neutralizing such attacks.
Secondly, verify that Secure Boot is enabled and that the revocation list is current. Secure Boot is designed to validate the signatures of boot components, preventing most unauthorized bootloaders. However, it can leave external media bootable, and compromised signed shims can still facilitate bypasses. ESET research in July 2026 highlighted 11 legacy Microsoft-signed UEFI shims that allowed untrusted code to execute at boot on any machine trusting Microsoft’s third-party certificate. While Microsoft has since revoked these in its June 9, 2026 DBX update, laptops that have not received this update remain vulnerable. Therefore, it is imperative to lock the boot order at the UEFI level, disable one-time boot menus, and implement a BIOS administrator password that secures both the setup utility and any boot-override keys. Meyers’ observation that many of these settings are often unchecked due to the perceived inconvenience of implementation underscores the critical need for proactive policy enforcement.
Thirdly, issue dedicated travel-only devices for international conferences. These devices should be strictly configured with no access to production systems, no saved credentials for internal tools, and no persistent VPN configurations. As Meyers succinctly put it, referencing an old DEF CON adage, "If they can get their hands on it, they can own it." Falcon can only detect FlowCloud after the operating system boots; the critical exposure period remains the hours between the USB write and the next login, during which the compromised laptop sits closed and seemingly secure.
"It’s cheap to buy a couple of laptops and a couple of phones," Meyers concluded, emphasizing that the controls necessary to close this significant security window are primarily a handful of firmware settings and the deployment of dedicated travel devices. The ultimate question for organizations remains whether these readily available, yet often neglected, defenses have been implemented before the next sophisticated physical intrusion occurs.
