
 By admin
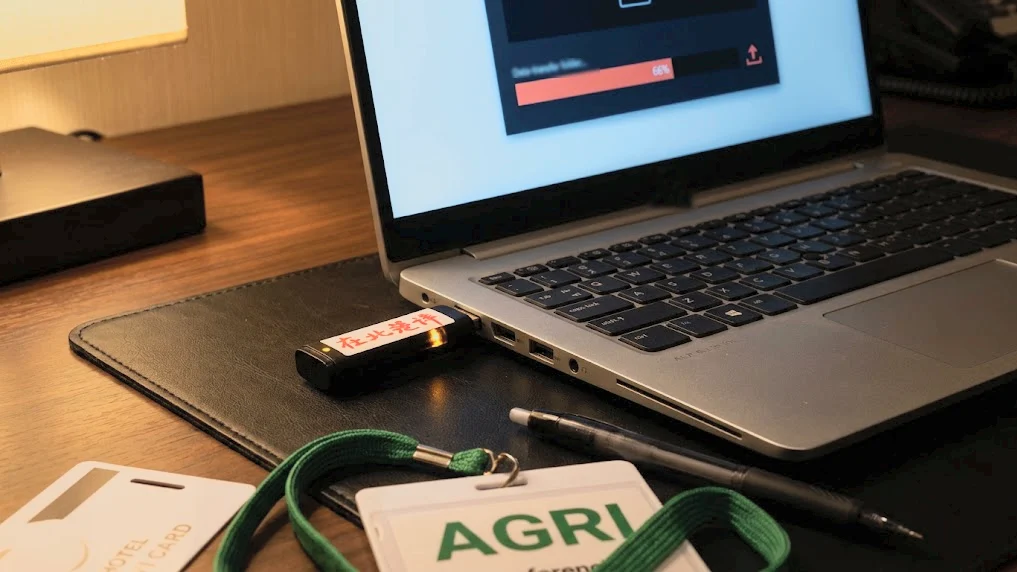
In a sophisticated and alarming campaign, a Chinese state-linked hacking group, identified by CrowdStrike as OVERCAST PANDA, successfully infiltrated executive laptops at an agricultural industry conference held on Hainan Island this past spring. The breach, meticulously detailed in CrowdStrike’s 2026 Threat Hunting Report, eschewed conventional cyberattack vectors like phishing or network exploitation. Instead, the adversaries employed a chillingly direct method: gaining physical access to hotel rooms and compromising the devices through a USB stick while their unsuspecting targets were away, most notably during evening dinner hours.
The groundbreaking operation, disclosed by CrowdStrike at Fal.Con 2026, involved intruders entering hotel rooms and, with precise timing, writing a backdoor malware named FlowCloud directly to each laptop’s storage. According to Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, the intrusion timeline indicates an individual entered one room around 8 p.m. local time and a second room by 9:57 p.m. The machines were then rebooted and left undisturbed, leaving no trace of network intrusion, phishing attempts, or compromised credentials through login pages. The malware, FlowCloud, is not new; Proofpoint documented its use in 2020, delivered via phishing to the U.S. utilities sector. Similarly, NTT Security’s Security Operations Center has tracked USB-delivered infections targeting overseas branches of Japanese organizations since early 2022, highlighting a persistent threat vector.
CrowdStrike’s OverWatch team intervened and disrupted the intrusions, assessing that OVERCAST PANDA is highly likely to continue such operations. The report places these specific intrusions between March and May 2026, with timestamps corroborated by Meyers in an interview with VentureBeat. What distinguishes this campaign is the strategic combination of physical hotel room entry by a state intelligence service with direct malware deployment, bypassing the need for user interaction with a USB drive after initial infection. This method, often referred to as an "evil maid attack" since its demonstration by Joanna Rutkowska in 2009, is remarkably rare among the 290 named adversaries tracked by CrowdStrike. While other groups, like MUSTANG PANDA, utilize a dropped USB stick that the victim physically inserts, OVERCAST PANDA’s approach signifies a significant escalation in stealth and precision.
Upon powering on their laptops the following morning, the executives unknowingly initiated the compromised systems. A pre-configured trigger within the operating system would then activate FlowCloud, commencing its malicious payload. This included keylogging, screen capture, file collection, and the harvesting of sensitive credentials, effectively granting the attackers deep access to the executives’ digital lives. Meyers elaborated to VentureBeat, "We have the visibility once the machine boots up." The FlowCloud malware is designed to load after the operating system initiates, often triggered by a registry key. It is at this point that CrowdStrike’s Falcon sensor detects the malicious process. The critical vulnerability, however, lies in the window between the USB write operation and the subsequent system boot – a period where the laptop remains compromised and undetected.
The timing of CrowdStrike’s disclosure of this vulnerability gap, just a month before the company announced its slate of AI security products at Fal.Con 2026 – including Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway – underscores the urgency of addressing such advanced threats. These new AI-powered security solutions aim to tackle the evolving threat landscape, but the OVERCAST PANDA incident highlights a fundamental gap that traditional security tools struggle to address.
Why Existing Security Tools Failed to Detect the Initial Compromise
The effectiveness of OVERCAST PANDA’s attack lies in its ability to bypass conventional security measures at their most fundamental levels. Endpoint Detection and Response (EDR) solutions, for instance, require the operating system to be loaded and their agent to be running to detect threats. Multi-Factor Authentication (MFA) and phishing awareness training are designed to prevent unauthorized access during login attempts or in response to malicious emails, respectively. AI-driven agent security focuses on securing the agents themselves. However, in this scenario, OVERCAST PANDA’s initial compromise occurred below the operating system, beneath the EDR agent, and prior to any authentication stack being engaged.
While Falcon successfully detected FlowCloud once its process began after the system reboot, the implant and its activation mechanism were already firmly entrenched on the laptop’s storage. This highlights a critical limitation: existing security tools are primarily designed to monitor activity within a running operating system and user session. Threats that exploit the boot process itself, or gain physical access to dormant hardware, can operate in a stealthy shadow zone.
"Hotel entry is a very common thing," Meyers observed, speaking to the ubiquity of physical access to transient environments. "Talk to any corporate physical security person. They’re generally aware of hotel entry, but I think what is unique is the combination of hotel entry with deployment of malware." This strategic fusion of a common, often overlooked, physical vulnerability with sophisticated malware deployment is what made the OVERCAST PANDA campaign so potent.
Meyers posits that China’s Ministry of State Security (MSS) is likely behind OVERCAST PANDA. He suggests that the individuals performing the room intrusions are either MSS or Ministry of Public Security officers, or potentially bribed or compelled hotel housekeeping staff. The report also reveals a parallel mid-2026 intrusion targeting a U.S.-based media professional using identical tradecraft, indicating a broader and more persistent intelligence-gathering operation. The specific targeting of an agricultural conference aligns with intelligence collection priorities frequently linked to China’s national five-year plans, which often emphasize technological and resource self-sufficiency.
CrowdStrike’s Fal.Con Announcements and the Dawn of Runtime Security
At Fal.Con 2026, CrowdStrike unveiled a suite of AI-powered security solutions designed to address the evolving threat landscape. Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to introduce SafeMind, an agentic cybersecurity system built upon Nvidia’s Nemotron open models and CrowdStrike’s extensive threat intelligence. This collaboration signals a significant push towards leveraging AI for proactive defense. Meyers also highlighted the escalating volume of vulnerabilities, noting that 7,400 CVEs were registered in June 2026, a staggering 96% increase over the previous year, with CrowdStrike responsibly disclosing approximately 30% of these.
Falcon Guardian, CrowdStrike’s runtime security layer for AI agents on endpoints, was officially launched during the conference. This product is specifically designed to monitor and protect AI agents from malicious prompts and exploitation. AI Gateway, a related capability, is set to ship as a hosted service in September, with a hybrid version to follow. AJ Shipley, CrowdStrike’s chief product officer, confirmed that a SafeMind model will be integrated into Guardian within weeks, enhancing its ability to detect malicious prompts.
The threats these new products aim to counter are quantified in CrowdStrike’s report. AI agent-triggered detection leads have grown at 2.5 times the rate of human-triggered leads, according to OverWatch’s analysis. Cloud-conscious eCrime activity has surged by an alarming 171% over the reporting period. Vishing (voice phishing) intrusions have doubled in the first half of 2026 compared to the latter half of 2025. The eCrime group SNARKY SPIDER, for example, has demonstrated a rapid transition from account takeover to data exfiltration in under five minutes after compromising SSO-integrated SaaS applications. Crucially, every one of these escalating threats is network-based and relies on a running operating system, an active user session, or a live cloud workload – precisely the assumptions that OVERCAST PANDA’s physical access attack circumvents.
The Fundamental Controls: Firmware and Policy as the Bulwark
While the OVERCAST PANDA campaign represents a sophisticated new tactic, the solutions to counter it are not new; they are, however, often inconvenient. "It’s a solvable problem," Meyers stated. "It’s just an inconvenient solution, which means that a lot of people don’t do it." The controls that would have effectively blunted this specific attack vector are rooted in firmware settings and organizational policy, harkening back to foundational security principles.
CrowdStrike itself has offered firmware attack detection and BIOS settings auditing capabilities through its Falcon sensor since May 2019, including Dell SafeBIOS integration. This functionality, capable of auditing security-related BIOS settings on laptops, has been available for seven years, making its application to travel devices a matter of policy and decision-making, rather than a product gap.
The core vulnerabilities exploited by OVERCAST PANDA are addressable through a combination of readily available, albeit sometimes overlooked, security measures. Disabling external boot in UEFI (Unified Extensible Firmware Interface) is the most direct way to remove the USB boot vector. A strong BIOS administrator password is essential to prevent unauthorized changes to these settings. Pre-boot authentication, requiring a PIN or USB key before the operating system loads, ensures that even if a foreign boot environment is loaded, the encrypted data volume remains inaccessible until the human factor intervenes. Firmware monitoring, while an after-the-fact detection method, can identify tampering that may have occurred.
Meyers offered a stark piece of advice: "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He recounted using temporary laptops and disposable email accounts for overseas travel during his tenure at CrowdStrike, making a point to wipe devices upon return. The exposure, he warned, begins even before reaching the destination, with potential device seizures and compelled logins at customs. The perceived security of hotel safes, he noted, is often illusory, with intelligence services possessing "master keys" to bypass them.
The Prioritization Paradox: Scale vs. Targeted Precision
The growth of intrusions tracked by CrowdStrike OverWatch has seen a steady increase, with approximately 4% growth in the reporting period following a significant 27% rise the previous year. This plateau, CrowdStrike attributes to a strategic shift by threat actors towards more complex and resource-intensive campaigns, exemplified by the OVERCAST PANDA hotel room operation.
However, when asked to compare the OVERCAST PANDA hotel room campaign with the rapid, AI-powered exploits of eCrime groups like REVENANT SPIDER – which compromised 17 victims with custom web shells in just 48 minutes – Meyers expressed greater concern for the latter. His reasoning is rooted in the fundamental principle of scale. "You can’t intrude on hotel rooms at scale," he emphasized. "You can’t intrude on physical devices at scale. And even then, it’s just one device." Physical-access tradecraft, while highly effective against specific, high-value targets, is inherently limited in its reach. The individual in the room is the target, and such intrusions rarely offer the pivot points for widespread network compromise.
In contrast, REVENANT SPIDER’s AI-driven attacks operate at network speed, capable of infecting numerous machines rapidly. This scalability is a primary driver of security budget allocation. Organizations tend to prioritize defenses against threats that can impact the largest number of systems. Consequently, the most insidious, yet less scalable, threats like the OVERCAST PANDA operation, which exploit fundamental physical security weaknesses, often receive less attention and fewer resources, even though they can be devastatingly effective against targeted individuals. The executives at the Hainan Island agricultural conference, however, were precisely the intended targets of a state intelligence service that deliberately chose an unscalable method because it offered a guaranteed avenue of access where network-based attacks would likely fail.
The Conference as a Threat Model: A Fractured Security Landscape
The executives attending conferences are effectively the living embodiment of the campaign’s threat model. Their laptops, often carrying sensitive production access, become prime targets. The vendors showcasing their wares on the Las Vegas convention floor were largely promoting runtime protection solutions – the same class of security that begins its work only after the machine boots, leaving that critical window of vulnerability exposed.
The true organizational challenge lies in the fragmentation of security responsibilities. Falcon Guardian might be managed by one team, while BIOS configuration on travel laptops falls under the purview of another. The Agentic Identity Provider is deployed by identity governance, yet the decision about whether executives should carry production-access machines to international conferences rests with yet another group. Furthermore, the budget line item for cloud-threat defense bears no relation to the policy governing travel-device security. This organizational fracture creates siloes where critical security controls remain unaddressed. Meyers, drawing from his own experience, recounted instances where companies planned board meetings in sensitive international locations without adequately considering the inherent security risks.
Essential Pre-Trip Security Audits for Executives
To mitigate the risk of similar "evil maid" attacks, a proactive and rigorous approach to executive travel security is paramount. Security leaders must prioritize auditing every executive laptop for its USB boot status. If a device can be booted from USB immediately, it possesses the same critical vulnerability that OVERCAST PANDA exploited. For Windows laptops, the primary target of FlowCloud, specific actions are necessary:
-
Enforce Full-Disk Encryption with Pre-Boot Authentication: While BitLocker with TPM-only configuration offers some protection, it has been identified as a weak point against physical access. Researchers have demonstrated the ability to extract the volume master key from the LPC bus using inexpensive hardware. OVERCAST PANDA’s ability to write a backdoor directly to the Windows volume suggests that target machines were either unencrypted or protected by a configuration that was bypassed. Implementing pre-boot authentication with a PIN or USB key forces a human interaction step before storage becomes accessible, rendering the backdoor and its trigger inert until the authorized user provides credentials.
-
Verify Secure Boot and Update Revocation Lists: Secure Boot is designed to validate the signatures of boot components, preventing most unauthorized bootloaders. However, it can leave external media bootable, and signed shims can still facilitate bypasses. ESET’s findings on legacy Microsoft-signed UEFI shims, which allowed untrusted code to run at boot, highlight the importance of up-to-date revocation lists. Laptops that have not received critical security updates, such as Microsoft’s June 9, 2026 DBX update, may still trust these compromised shims. Therefore, locking the boot order at the UEFI level, disabling one-time boot menus, and securing the setup utility and any boot-override keys with a robust BIOS administrator password are critical steps. These settings are often unchecked due to their perceived inconvenience.
-
Issue Dedicated Travel Devices: For international conferences, organizations should issue travel-specific devices that are completely isolated from production systems. These devices should have no saved credentials for internal tools and no persistent VPN configurations. This ensures that even if compromised, the attacker’s access is limited to the ephemeral data on the travel device itself.
"If they can get their hands on it, they can own it," Meyers reiterated, referencing a well-known adage from the DEF CON security conference. CrowdStrike’s Falcon sensor catches FlowCloud only after the system boots, meaning the window of exposure is the critical period between the USB write and the next user login, during which the laptop remains closed and compromised. The solution, Meyers concluded, is relatively simple and inexpensive: "It’s cheap to buy a couple of laptops and a couple of phones." The controls that close the vulnerability window are a handful of firmware settings and the deployment of dedicated travel hardware. The ultimate question remains whether organizations are willing to implement these fundamental, yet inconvenient, safeguards before the next sophisticated attack unfolds.
