
 By admin
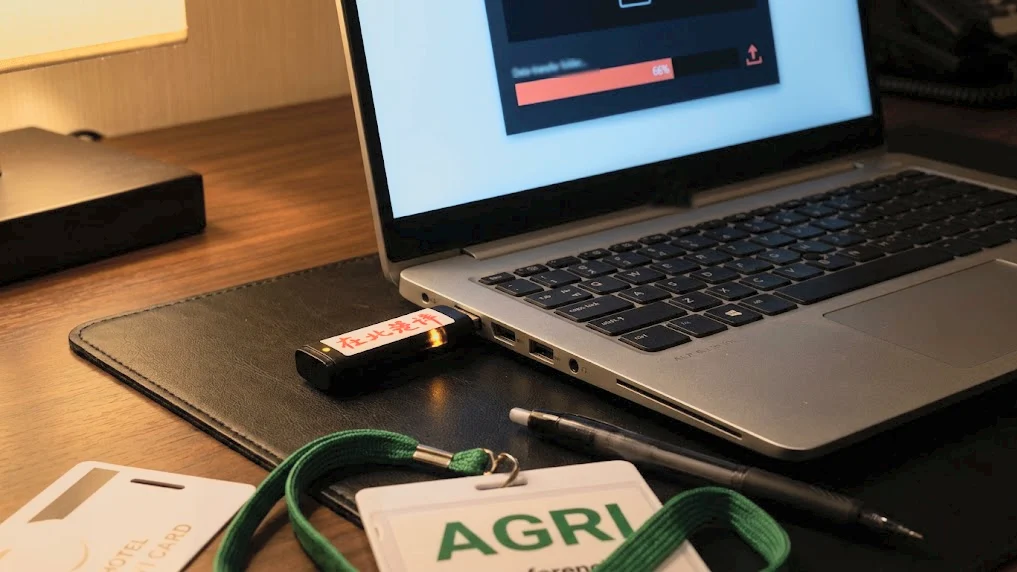
In a brazen and sophisticated cyber-attack, a Chinese state-linked hacking group, tracked by cybersecurity firm CrowdStrike as OVERCAST PANDA, successfully infiltrated executive laptops attending an agricultural industry conference on Hainan Island this spring. The modus operandi was particularly alarming, eschewing conventional phishing or network-based breaches for a far more intrusive method: physical access to hotel rooms. While unsuspecting executives were attending evening dinners, attackers reportedly entered their hotel rooms, directly compromised their unattended laptops by booting them from a USB stick, and installed sophisticated malware. This novel approach, detailed in CrowdStrike’s 2026 Threat Hunting Report, highlights a critical vulnerability in traditional cybersecurity defenses that rely heavily on network perimeter security and endpoint protection once the operating system is active.
CrowdStrike’s analysis, corroborated by interviews with Adam Meyers, Senior Vice President of Counter Adversary Operations, revealed a meticulously planned operation. The timeline indicates intrusions occurring between 8 p.m. and 9:57 p.m. local time during the conference. Attackers gained entry to at least two hotel rooms, meticulously writing a backdoor malware named FlowCloud directly to each laptop’s storage. The machines were then rebooted, leaving no trace of a network intrusion, no phishing emails sent, and no credentials compromised through typical login page attacks. The compromised laptops were left seemingly untouched, awaiting their owners’ return.
The FlowCloud malware itself is not new. Proofpoint documented its use in 2020, delivered via phishing against U.S. utilities, and NTT Security’s Security Operations Center (SOC) has been tracking USB-delivered infections by other actors since early 2022. However, OVERCAST PANDA’s deployment method represents a significant evolution. Security researchers have long categorized this type of physical-access tampering with an unattended laptop as an "evil maid attack," a term coined by Joanna Rutkowska in 2009. These attacks are characterized by gaining physical access to a device and making modifications that compromise its security, often using bootable media like USB drives.
Meyers emphasized that while physical access operations are relatively rare among the 290 named adversaries CrowdStrike tracks, OVERCAST PANDA’s execution was particularly noteworthy. Unlike other groups, such as MUSTANG PANDA, which relies on victims to unknowingly plug in a dropped USB stick, this operation involved direct physical entry into a secure hotel environment. The novelty lies in the combination of state intelligence services orchestrating hotel room entry with direct malware deployment through bootable media, bypassing the user entirely. The attackers’ goal was to implant the malware and its trigger mechanism onto the laptop’s storage before the user even powered it on the next morning.
Once the executives booted their laptops, a pre-programmed trigger would activate FlowCloud, initiating a suite of malicious activities. These included keylogging to capture typed information, screen capture to record user activity, file collection for data exfiltration, and credential harvesting to steal sensitive login information. Meyers explained that CrowdStrike’s Falcon sensor could detect FlowCloud once its process started after the operating system loaded. The critical window of vulnerability, however, was the period between the USB write and the subsequent boot-up – hours during which the laptop remained compromised and undetected. This gap, between the physical compromise and the operational detection, is where the threat actor operated with impunity.
CrowdStrike’s disclosure of this campaign came shortly before its announcement of a new suite of AI security products at Fal.Con 2026, a significant timing that underscores the evolving threat landscape. The report highlights how existing security tools, such as Endpoint Detection and Response (EDR), Multi-Factor Authentication (MFA), and phishing awareness training, were rendered ineffective at the point of compromise. EDR solutions require the operating system and their agent to be running, MFA only activates during a login attempt, and phishing training is designed to prevent users from falling for deceptive emails. OVERCAST PANDA’s method bypassed all these layers by operating at the firmware and storage level, below the active OS and its security agents.
Meyers stated that while hotel entry is a common concern for corporate physical security teams, the unique aspect of this campaign was its fusion with advanced malware deployment. He posited that China’s Ministry of State Security (MSS) likely directs OVERCAST PANDA, with the operatives being MSS or Ministry of Public Security officers, or even compromised hotel staff. The report also noted a similar intrusion targeting a U.S.-based media professional using the same tradecraft in mid-2026. The targeting of an agricultural conference aligns with collection priorities linked to China’s ongoing five-year plans, suggesting a strategic intelligence gathering operation.
At Fal.Con 2026, CrowdStrike unveiled several new AI-driven security solutions designed to address the increasingly complex threat landscape. Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to announce SafeMind, an agentic cybersecurity system built on Nvidia Nemotron open models and CrowdStrike’s extensive threat intelligence. CrowdStrike President Mike Sentonas also introduced Falcon Guardian, a runtime security layer for AI agents on endpoints, and AI Gateway, a hosted service for AI security. These announcements reflect the growing sophistication of cyber threats, with AI agents increasingly becoming both attack vectors and defense mechanisms.
The report detailed alarming trends that these new solutions aim to combat. AI agent-triggered detection leads grew at 2.5 times the rate of human-triggered leads, indicating a significant shift in threat actor behavior. Cloud-conscious eCrime activity surged by an astonishing 171% during the reporting period. Vishing (voice phishing) intrusions doubled in the first half of 2026 compared to the second half of 2025, with eCrime groups like SNARKY SPIDER demonstrating alarming agility, moving from account takeover to data exfiltration in under five minutes after compromising Single Sign-On (SSO) integrated SaaS applications. These threats, while diverse, predominantly rely on network-based vectors, assuming a running operating system, an active user session, or a live cloud workload.
The OVERCAST PANDA hotel room attack, however, operates outside these assumptions. The controls that would have effectively countered this specific campaign are not new or technologically complex; rather, they are foundational security practices related to firmware and policy enforcement. Meyers emphasized that this is a "solvable problem," though it requires inconvenient but necessary measures. CrowdStrike itself has offered firmware attack detection and BIOS settings auditing through its Falcon sensor since May 2019, including integrations with Dell SafeBIOS. The capability to audit security-related BIOS settings on laptops has existed within their platform for seven years, meaning the gap exploited by OVERCAST PANDA was a policy decision not to implement these controls on travel devices.
To mitigate such "evil maid" attacks, organizations need to enforce stringent firmware-level security. This includes disabling external boot in UEFI settings, which directly removes the USB boot vector. A robust BIOS administrator password is crucial to prevent unauthorized changes to these settings. Furthermore, implementing pre-boot authentication (PBA) ensures that even if a foreign boot environment is loaded, the encrypted volume remains inaccessible until a human provides a PIN or key. Firmware monitoring can also detect tampering after the fact.
Meyers offered a stark warning: "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He advocated for using temporary laptops and disposable email accounts for overseas travel, wiping devices upon return. The risk begins even before reaching the hotel, as customs officials can seize devices and compel logins. The security of hotel safes, often perceived as secure, was also called into question, with Meyers suggesting they offer little true protection against determined actors.
While the OVERCAST PANDA operation was highly targeted and unscalable, Meyers expressed greater concern about the broader trend of network-speed, AI-powered intrusions. He contrasted the hotel room campaign with the REVENANT SPIDER case, where an eCrime group used AI to compromise 17 victims with custom web shells in just 48 minutes. The reason for his greater concern lies in scalability: "You can’t intrude on hotel rooms at scale. You can’t intrude on physical devices at scale. And even then, it’s just one device." Network-based attacks, especially those amplified by AI, can impact thousands or millions of machines, making them a more significant threat to the average enterprise and attracting larger security budgets.
However, the targeted nature of the OVERCAST PANDA attack underscores a different kind of threat. The executives at the agricultural conference were specifically chosen targets of a state intelligence service that opted for a slow, deliberate, and unscalable method precisely because it bypasses the defenses that protect against faster, network-based attacks. The conference itself, in this context, became the threat model – a gathering of high-value targets in a less controlled environment.
The vendors at Fal.Con 2026 were showcasing runtime protection for AI agents, addressing the very gap that exists once a machine boots. The fundamental problem, however, lies in organizational fracture. Different teams manage different security domains: Falcon Guardian for AI agents, BIOS configuration for travel laptops, identity governance for Agentic IdP, and cloud threat defense budgets are often siloed from travel device policies. This fragmentation prevents a holistic security approach. Meyers’ personal experience highlighted this disconnect, recalling conversations with companies planning board meetings in potentially insecure international locations without adequate security considerations for devices.
To proactively defend against such attacks before the next international trip, security leaders must take immediate action. A critical first step is to audit every executive laptop for USB boot status. If a device can be booted from USB, it possesses the same vulnerability exploited by OVERCAST PANDA. For Windows laptops, which FlowCloud targets, enforcing full-disk encryption with pre-boot authentication is paramount. BitLocker, when configured with TPM-only, has been shown to be a weak point against physical access, as demonstrated by SCRT researchers and the Dolos Group, who were able to extract volume master keys. OVERCAST PANDA’s ability to write a backdoor and its trigger to the Windows volume suggests either unencrypted drives or compromised encryption configurations. Pre-boot authentication with a PIN or USB key introduces a necessary human step before data storage becomes accessible, effectively neutralizing the threat.
Furthermore, verifying that Secure Boot is enabled and that the revocation list is current is essential. While Secure Boot validates boot components, legacy UEFI shims, if not updated, can still allow untrusted code to run. Microsoft’s revocation of such shims in its June 9, 2026 DBX update means that laptops that have not received this update remain vulnerable. Locking the boot order at the UEFI level, disabling one-time boot menus, and setting a strong BIOS administrator password that covers both the setup utility and any boot-override key are crucial firmware-level controls. These settings, though inconvenient, are fundamental to securing the boot process.
Finally, issuing travel-only devices for international conferences, devoid of access to production systems, saved credentials for internal tools, and persistent VPN configurations, significantly reduces the attack surface. As Meyers succinctly put it, citing an old DEF CON adage, "If they can get their hands on it, they can own it." The period between the USB write and the next login, while the laptop is closed and compromised, represents the critical window of exposure. The solution, Meyers concluded, is relatively inexpensive: a few spare laptops and phones, coupled with a handful of firmware settings. The real challenge lies in whether organizations are willing to implement these essential, albeit old-fashioned, controls to close the security gap that state-sponsored actors like OVERCAST PANDA are so adept at exploiting.
