 By admin
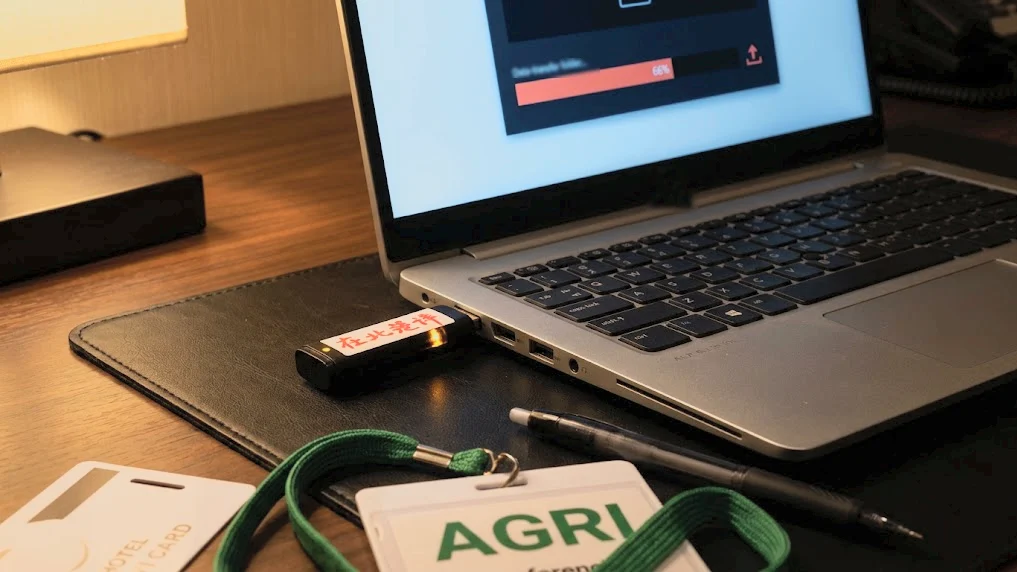
In a sophisticated and unsettling operation, a Chinese state-linked hacking group, tracked by cybersecurity firm CrowdStrike as OVERCAST PANDA, successfully compromised executive laptops attending an agricultural industry conference on Hainan Island this spring. This campaign eschewed conventional cyberattack vectors like phishing emails or network intrusions, opting instead for a daring physical infiltration of hotel rooms. While attendees were away at dinner, operatives gained unauthorized access to their accommodations, booting the unattended laptops from a USB stick to install malicious software.
CrowdStrike, a leading cybersecurity firm, revealed the details of this campaign in its comprehensive 2026 Threat Hunting Report. The group’s meticulous timeline, shared with VentureBeat during Fal.Con 2026, paints a chilling picture of the operation. Between March and May 2026, intruders entered hotel rooms around 8 p.m. local time, with a second intrusion occurring by 9:57 p.m. During these brief windows, they meticulously wrote a backdoor known as FlowCloud directly onto each laptop’s storage. The machines were then rebooted and left as they were found, leaving no discernible trace of network intrusion, phishing attempts, or stolen credentials from login pages. Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, confirmed these timestamps and the operation’s details.
The FlowCloud malware itself is not new; Proofpoint had documented its use in 2020, delivered via phishing against the U.S. utilities sector. More recently, NTT Security’s Security Operations Center (SOC) had been tracking USB-delivered FlowCloud infections at overseas branches of Japanese organizations since early 2022. However, the method of deployment employed by OVERCAST PANDA represents a significant escalation and a departure from typical threat actor methodologies.
Security researchers have long recognized the concept of physical-access tampering with unattended laptops as an "evil maid attack," a term coined by Joanna Rutkowska in 2009 following her demonstration of such an attack using a bootable USB stick. Despite the long-standing awareness of this vulnerability, CrowdStrike’s analysis indicates that physical-access operations are relatively rare among the 290 named adversaries the company tracks. While other groups, such as MUSTANG PANDA, have employed similar tactics, their approach typically involves tricking the victim into plugging in a dropped USB stick. What Meyers identified as novel in the OVERCAST PANDA operation is the confluence of direct physical access, facilitated by state intelligence services, with the direct deployment of malware via a bootable USB. This bypassed the need for user interaction to execute the malicious code, significantly reducing the attack’s detectability.
The intended impact of this meticulous infiltration became clear the following morning. When the executives powered on their laptops, a pre-programmed trigger would activate FlowCloud. This would initiate a cascade of malicious activities, including keylogging, screen capture, file collection, and the harvesting of sensitive credentials. Meyers explained to VentureBeat, "We have the visibility once the machine boots up." The FlowCloud malware was designed to load after the operating system initiated, often through a registry key or similar trigger, at which point CrowdStrike’s Falcon sensor could detect its activity. The critical vulnerability exploited was the silent window of compromise – the hours between the USB write and the subsequent reboot, during which the laptop sat compromised and undetected before the executive logged back in.
CrowdStrike’s disclosure of this campaign occurred just a month before the company announced its new suite of AI security products at Fal.Con 2026. These products include Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway, all designed to address evolving threat landscapes.
Why Existing Security Tools Missed the ‘Evil Maid’ Attack
The effectiveness of OVERCAST PANDA’s strategy lies in its ability to bypass virtually every layer of modern endpoint security. Endpoint Detection and Response (EDR) solutions, for instance, require the operating system to be loaded and their agent to be running to detect threats. Multi-Factor Authentication (MFA) solutions are designed to protect against unauthorized logins. Phishing training aims to educate users about deceptive emails, and AI agent security focuses on securing the agents themselves. OVERCAST PANDA circumvented all of these by compromising the system at a level below the running OS, below the EDR agent, and below the authentication stack. While CrowdStrike’s Falcon platform successfully detected FlowCloud once its process began post-boot, the implant and its execution trigger were already deeply embedded on the disk, making immediate remediation challenging.
Meyers highlighted the seemingly innocuous nature of the initial point of access. "Hotel entry is a very common thing," he stated, adding that while corporate physical security teams are generally aware of hotel entry risks, the combination of this physical access with direct malware deployment is what sets this campaign apart.
CrowdStrike’s intelligence suggests that China’s Ministry of State Security (MSS) is likely behind OVERCAST PANDA. Meyers posited that the individuals directly involved in the room intrusions were either MSS officers, agents of the Ministry of Public Security, or compromised hotel housekeeping staff. The report also detailed a separate intrusion in mid-2026 that targeted a U.S.-based media professional using the same sophisticated tradecraft. The specific targeting of an agricultural conference aligns with intelligence collection priorities that Meyers has linked to China’s national five-year plans, suggesting a strategic focus on economic and technological advancement within this sector.
CrowdStrike’s Fal.Con Announcements and the Dawn of Runtime Security
The annual Fal.Con conference served as a platform for CrowdStrike to unveil several groundbreaking AI-driven security solutions. In a notable collaboration, Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to introduce SafeMind, an agentic cybersecurity system built upon Nvidia’s Nemotron open models and CrowdStrike’s extensive threat intelligence. During his presentation, Meyers underscored the escalating threat landscape, revealing that 7,400 CVEs (Common Vulnerabilities and Exploits) were registered in June 2026, representing a staggering 96% increase over June 2025. CrowdStrike itself was responsible for the responsible disclosure of 2,400 of these vulnerabilities, approximately 30% of the total registered that month.
CrowdStrike President Mike Sentonas announced that Falcon Guardian, the company’s new runtime security layer for AI agents on the endpoint, became available immediately. AI Gateway, initially presented as a capability within Guardian, is slated for release as a hosted service in September, with a hybrid version to follow. AJ Shipley, CrowdStrike’s chief product officer, further elaborated that a SafeMind model will be embedded within Guardian within the coming weeks, specifically designed to detect malicious prompts used in AI-driven attacks.
The threats these new products are designed to combat are increasingly potent and widespread. CrowdStrike’s OverWatch team reported that AI agent-triggered detection leads grew at 2.5 times the rate of human-triggered leads. Cloud-conscious eCrime activity saw a dramatic surge of 171% during the reporting period. Vishing (voice phishing) intrusions doubled in the first half of 2026 compared to the latter half of 2025. Notably, the eCrime group SNARKY SPIDER demonstrated an alarming agility, transitioning from account takeover to data exfiltration in under five minutes after compromising SSO-integrated SaaS applications.
Crucially, all of these escalating threats operate within the traditional cybersecurity paradigm, relying on a running operating system, an active user session, or a live cloud workload. The OVERCAST PANDA campaign, however, operates in a fundamentally different domain, exploiting a gap that predates these active states.
The Underrated Power of Firmware and Policy Controls
"It’s a solvable problem," Meyers asserted regarding the ‘evil maid’ vulnerability, "It’s just an inconvenient solution, which means that a lot of people don’t do it." The controls that would have effectively thwarted the OVERCAST PANDA campaign are not new or complex; they are foundational security measures that have been available for years. CrowdStrike itself has offered firmware attack detection and BIOS settings auditing through its Falcon sensor since May 2019, including integrations with Dell SafeBIOS that surface BIOS verification telemetry directly in the Falcon console. The capability to audit security-related BIOS settings on the laptops executives carry has been present within the platform for seven years. The critical factor is the decision to implement these controls, particularly for devices used in high-risk travel scenarios.
The fundamental controls that could have blunted the OVERCAST PANDA campaign are inexpensive and target different aspects of the attack chain. Disabling external boot capabilities within the UEFI (Unified Extensible Firmware Interface) firmware is paramount, effectively removing the USB-based entry vector. A robust BIOS administrator password is essential to keep these critical firmware settings locked down and prevent unauthorized modifications. Pre-boot authentication, requiring a PIN or USB key before the operating system even begins to load, ensures that even if a foreign boot environment is established, the encrypted data volume remains inaccessible until a human user provides the necessary credentials. Furthermore, firmware monitoring can detect tampering after the fact, providing an audit trail.
Meyers offered a stark piece of advice for executives traveling internationally: "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He recounted his own practice of using temporary laptops and disposable email accounts for overseas trips, ensuring that all devices were wiped upon return. The risk, he noted, begins even before departure, at customs, where officials can seize devices and compel logins. Even hotel safes, he ominously concluded, are not as secure as they appear, with intelligence services possessing the means to bypass them.
The Persistent Challenge of Scale in Security Prioritization
CrowdStrike’s OverWatch team observed a roughly 4% increase in reported intrusions during the reporting period, following a substantial 27% rise the previous year. This plateau is attributed to a strategic shift by threat actors towards more complex and resource-intensive campaigns, exemplified by the OVERCAST PANDA hotel room operation.
However, Meyers expressed greater concern about network-based threats, particularly those amplified by AI. When asked to compare the OVERCAST PANDA hotel room campaign with the REVENANT SPIDER case – an eCrime group that used AI to compromise 17 victims with custom web shells in a mere 48 minutes – Meyers prioritized the latter. His reasoning was clear: "You can’t intrude on hotel rooms at scale. You can’t intrude on physical devices at scale. And even then, it’s just one device." Physical-access tradecraft, by its very nature, is inherently limited in its scalability. The target is an individual, and the intrusion rarely leads to a broader network pivot. In contrast, REVENANT SPIDER’s AI-driven approach operates at machine speed, posing a much more significant and pervasive threat to the average enterprise.
The reality of cybersecurity budgets is that they tend to follow the threats that impact the largest number of machines. This often leaves less attention and fewer resources for the more sophisticated, albeit less scalable, attack methods. Yet, the executives targeted in the Hainan Island incident were specifically chosen by a state intelligence service, which deliberately opted for a slow, unscalable method precisely because it offers a path to compromise where conventional network-based attacks would fail.
The Conference as a Threat Model and the Fragmentation of Security Controls
The executives attending conferences are the primary targets in campaigns like OVERCAST PANDA’s. The critical vulnerability lies in the fact that effective runtime security only begins once a machine boots up. The vendors exhibiting at Fal.Con 2026, showcasing their latest security solutions, were largely addressing this very gap in runtime protection for attendees whose own laptops carried the identical vulnerability.
A significant underlying problem is organizational fracture. The implementation of security controls is often siloed. Falcon Guardian, for example, might be managed by one team, while BIOS configuration for travel laptops falls under the purview of another. The Agentic Identity Provider could be rolled out under identity governance, while decisions about whether executives should carry production-access machines to international conferences might reside with a separate group. Furthermore, the budget allocation for cloud-threat defense typically has no connection to travel-device policies. This fragmentation creates blind spots and allows sophisticated attacks to slip through the cracks. Meyers, drawing from his own experiences, noted companies that plan board meetings in high-risk international locations without fully appreciating the security implications.
Essential Pre-Trip Security Measures for Leaders
Before embarking on their next international journey, security leaders must implement several critical auditing and control measures. First, every executive laptop must be audited for its USB boot status. If a device can be booted from USB in its current configuration, it possesses the same critical gap that OVERCAST PANDA exploited. For Windows laptops, the primary target of FlowCloud, specific steps are crucial.
Enforcing full-disk encryption with pre-boot authentication is paramount. While BitLocker is a standard feature, a TPM-only configuration has been identified as a weak point against physical access. Researchers have demonstrated methods to extract the volume master key from the LPC bus with inexpensive hardware. OVERCAST PANDA’s ability to write a backdoor and its post-boot trigger to the Windows volume strongly suggests that the targeted machines were either unencrypted or protected by a configuration that could be bypassed. Pre-boot authentication, requiring a PIN or USB key, forces a human step before the storage becomes readable, thereby rendering such physical-access modifications inert.
Verifying that Secure Boot is enabled and that its revocation list is current is also essential. Secure Boot validates the signatures of boot components, blocking most unauthorized bootloaders. However, it can still leave external media bootable, and signed shims can be exploited to bypass these protections. Recent research has highlighted legacy Microsoft-signed UEFI shims that allowed untrusted code to run at boot on machines that still trusted Microsoft’s third-party certificate. While Microsoft has since revoked these, laptops that have not received the latest updates remain vulnerable. Therefore, locking the boot order at the UEFI level, disabling one-time boot menus, and setting a BIOS administrator password that covers both the setup utility and any boot-override keys are critical. Meyers indicated that many of these settings are often neglected due to the perceived inconvenience of implementation.
Finally, organizations should issue travel-specific devices for international conferences. These devices should have no access to production systems, no saved credentials for internal tools, and no persistent VPN configurations, thereby minimizing the potential impact of a compromise.
"If they can get their hands on it, they can own it," Meyers stated, echoing a well-known adage from the DEF CON security conference. CrowdStrike’s Falcon platform can detect FlowCloud, but only after it has been loaded post-boot. The period of exposure remains the hours between the USB write and the next login, during which the laptop sits closed and compromised. The solution, as Meyers suggests, is relatively inexpensive: "It’s cheap to buy a couple of laptops and a couple of phones." The controls that close this critical window are a handful of firmware settings and the strategic use of dedicated travel devices. The fundamental question remains whether organizations are willing to implement these measures proactively.
