 By admin
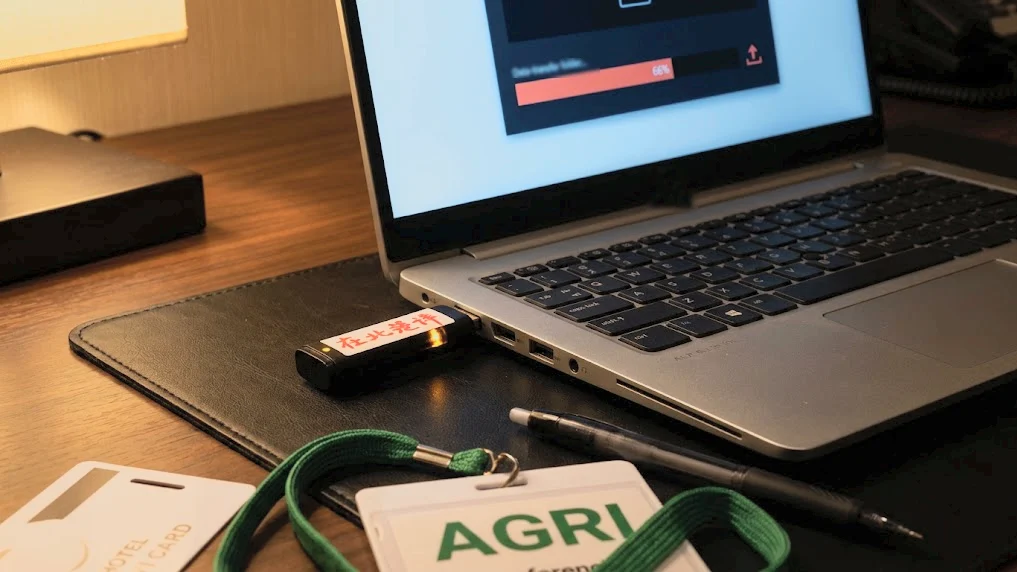
This spring, a sophisticated cyberattack unfolded not through the usual channels of phishing emails or network breaches, but via a more audacious and physically intrusive method: state-linked Chinese hackers infiltrated hotel rooms of executives attending an agricultural industry conference on Hainan Island, compromising their laptops by booting them from USB drives while the unsuspecting attendees were at dinner. The campaign, meticulously tracked by CrowdStrike and identified as the work of a group they designate OVERCAST PANDA, represents a chilling evolution in cyber warfare, targeting critical infrastructure and business leaders through an "evil maid attack" amplified by state-sponsored resources.
CrowdStrike, a leading cybersecurity firm, detailed this alarming operation in its 2026 Threat Hunting Report, offering a glimpse into the precise timeline and methodology employed by OVERCAST PANDA. According to Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, who shared key timestamps in an interview with VentureBeat at Fal.Con 2026, intruders gained access to at least two hotel rooms around 8 p.m. and 9:57 p.m. local time. Their objective was singular: to physically insert a USB drive into the targeted laptops, write a backdoor known as FlowCloud directly onto the machines’ storage, and then reboot them, leaving no trace of network intrusion, phishing attempts, or compromised credentials. This method bypasses many of the foundational security layers modern enterprises rely on.
The intrusions, dated between March and May 2026, highlight a disturbing trend. FlowCloud itself is not a new piece of malware; Proofpoint had documented its use in 2020, delivered via phishing campaigns targeting the U.S. utilities sector. More recently, NTT Security’s Security Operations Center (SOC) has been tracking USB-delivered infections of this malware at overseas branches of Japanese organizations since early 2022. However, the OVERCAST PANDA campaign’s novelty lies in the audacious combination of physical hotel room entry, executed by what is believed to be a state intelligence service, with direct malware deployment. This is a stark departure from the more common "dropped USB" scenarios, where victims are tricked into inserting the malicious drive themselves.
The term "evil maid attack," coined by security researcher Joanna Rutkowska in 2009, perfectly encapsulates this physical-access tampering technique. Rutkowska demonstrated the vulnerability of unattended laptops to bootable USB devices, a method that has historically been considered rare among the 290 named adversaries CrowdStrike monitors. While other groups, such as MUSTANG PANDA, have employed USB-based attacks, their approach typically relies on the victim inserting the drive. Meyers emphasized that the state intelligence service’s direct physical access to hotel rooms, coupled with the immediate deployment of malware via a bootable USB, marks a significant escalation.
Once the compromised laptops were powered on the following morning, the FlowCloud backdoor would activate. This triggered a cascade of malicious activities, including keylogging, screen capture, file collection, and credential harvesting, all conducted covertly while the executives were engaged in their daily work. Meyers explained that CrowdStrike’s Falcon sensor could detect FlowCloud once its process began after the operating system loaded, typically initiated by a registry key or similar trigger. However, the critical vulnerability lay in the silent window of compromise – the hours between the USB insertion and the next boot, during which the laptop remained physically accessible and undetected.
This revelation comes at a strategic moment, as CrowdStrike unveiled its suite of AI security products – Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway – at Fal.Con 2026, just a month after publishing the threat hunting report. The timing underscores the company’s proactive approach to addressing emerging threats, particularly those that circumvent traditional security measures.
Why Existing Security Tools Missed the Mark
The effectiveness of the OVERCAST PANDA attack lies in its ability to bypass fundamental security layers that most organizations rely on. Endpoint Detection and Response (EDR) solutions require the operating system to be loaded and the agent to be running to detect threats. Multi-Factor Authentication (MFA) only becomes relevant during a login attempt. Phishing awareness training is designed to prevent users from clicking malicious links or opening infected attachments. AI-powered agent security solutions are predicated on the agent’s presence and operation.
OVERCAST PANDA’s physical access method completely sidestepped these defenses at the point of entry. The initial compromise occurred below the operating system, below the EDR agent, and below the authentication stack. While Falcon was able to detect FlowCloud once it began its post-boot execution, the implant and its trigger mechanism were already deeply embedded in the laptop’s storage, rendering immediate remediation challenging.
"Hotel entry is a very common thing," Meyers noted, drawing a parallel to the everyday security concerns of corporate physical security teams. "But I think what is unique is the combination of hotel entry with deployment of malware." This suggests a deliberate and calculated strategy by the attackers to exploit an often-overlooked vulnerability in the travel security posture of high-profile individuals.
Meyers posited that China’s Ministry of State Security (MSS) is the likely orchestrator behind OVERCAST PANDA. He theorized that the individuals gaining physical access to the hotel rooms were either MSS or Ministry of Public Security officers, or possibly bribed or coerced hotel housekeeping staff. The report also detailed a separate mid-2026 intrusion targeting a U.S.-based media professional employing the same sophisticated tradecraft. The targeting of an agricultural conference is particularly significant, aligning with intelligence collection priorities linked to China’s ongoing five-year plans, which often encompass advancements in food security, biotechnology, and agricultural technology.
CrowdStrike’s Fal.Con Announcements and the Dawn of Runtime Security
The Fal.Con 2026 conference served as a platform for CrowdStrike to showcase its response to these escalating threats, particularly in the realm of artificial intelligence and advanced cyber defense. Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to unveil SafeMind, an agentic cybersecurity system built upon Nvidia’s Nemotron open models and CrowdStrike’s extensive threat intelligence. Meyers further highlighted the escalating threat landscape during his presentation, revealing that 7,400 CVEs were registered in June 2026, a staggering 96% increase over June 2025. CrowdStrike itself contributed approximately 30% of these disclosures through responsible disclosure initiatives, underscoring its role in identifying and mitigating vulnerabilities.
Falcon Guardian, CrowdStrike’s new runtime security layer for AI agents on endpoints, was announced to go live immediately, signifying a commitment to protecting the burgeoning AI ecosystem. AI Gateway, a hosted service with a hybrid option to follow, is slated for release in September. AJ Shipley, CrowdStrike’s chief product officer, confirmed that SafeMind models will be integrated into Guardian to detect malicious prompts within weeks, further bolstering the platform’s AI-specific defense capabilities.
These new offerings are designed to combat a rapidly evolving threat landscape. The report detailed significant surges in AI agent-triggered detection leads, which grew at 2.5 times the rate of human-triggered leads, according to OverWatch data. Cloud-conscious eCrime activity saw a dramatic 171% increase during the reporting period. Vishing intrusions doubled in the first half of 2026 compared to the latter half of 2025, with the eCrime group SNARKY SPIDER demonstrating an alarming ability to move from account takeover to data exfiltration in under five minutes after compromising SSO-integrated SaaS applications. Every one of these advanced threats, however, relies on a network-based infrastructure, assumes a running operating system, an active user session, or a live cloud workload – vulnerabilities that the OVERCAST PANDA attack so elegantly bypassed.
The Unconventional Controls: Firmware and Policy as the Bulwark
While the sophistication of the OVERCAST PANDA attack is undeniable, Meyers asserts that the solutions, though perhaps inconvenient, are fundamentally solvable. The controls that would have effectively blunted this campaign are not new, cutting-edge technologies, but rather established firmware settings and robust security policies.
CrowdStrike has, in fact, offered firmware attack detection and BIOS settings auditing through its Falcon sensor since May 2019, including a Dell SafeBIOS integration that surfaces BIOS verification telemetry within the Falcon console. The ability to audit security-related BIOS settings on laptops has been available for years, meaning the crucial step is the conscious decision to implement and enforce these policies, particularly for devices used in travel.
The core defenses against such physical-access attacks are surprisingly straightforward and cost-effective:
- Disabling External Boot in UEFI: This is the most direct countermeasure to prevent booting from unauthorized USB drives.
- BIOS Administrator Password: Implementing a strong BIOS administrator password ensures that unauthorized users cannot alter boot order settings or disable security features.
- Pre-Boot Authentication (PBA): When combined with full-disk encryption, PBA requires a human to provide a PIN or USB key before the encrypted volume can be accessed, even if a foreign boot environment is loaded. This prevents unauthorized access to the encrypted data.
- Firmware Monitoring: While this is an after-the-fact detection mechanism, it can alert administrators to tampering with firmware, providing crucial forensic data.
Meyers’ pragmatic advice to executives traveling internationally is stark: "Don’t bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He himself adopted a policy of using temporary laptops and disposable email accounts for overseas trips, thoroughly wiping devices upon return. The exposure, he warns, can begin even before departure, at customs, where officials have the authority to seize devices and compel logins. He also dismisses the perceived security of hotel safes, stating, "They have master keys to that stuff."
The Tyranny of Scale: Why Network Threats Dominate Security Budgets
The OVERCAST PANDA hotel room operation, while highly sophisticated and concerning for its targeted victims, represents a strategy that is inherently difficult to scale. CrowdStrike OverWatch observed a roughly 4% increase in intrusions during the reporting period, following a substantial 27% rise the previous year. This plateau is attributed to a strategic shift towards more complex and resource-intensive campaigns, such as the one detailed here.
When pressed to compare the OVERCAST PANDA campaign with the REVENANT SPIDER case—an eCrime group using AI to compromise 17 victims with custom web shells in a mere 48 minutes—Meyers unequivocally prioritized the latter as the more pervasive and concerning threat to the average enterprise. His reasoning is rooted in the fundamental difference in scalability. "You can’t intrude on hotel rooms at scale," he stated. "You can’t intrude on physical devices at scale. And even then, it’s just one device." Physical-access attacks are typically focused on a specific individual or device, and rarely offer a direct pivot to broader network compromise.
In contrast, network-speed, AI-powered intrusions, like those demonstrated by REVENANT SPIDER, can affect thousands or even millions of machines rapidly. Security budgets, by necessity, tend to follow the threats that impact the largest number of systems. This leaves the less scalable, but highly effective, physical-access tradecraft to exploit the gaps left by organizations focused on defending against high-volume network attacks. The executives targeted by OVERCAST PANDA were the specific focus of a state intelligence service, a service that deliberately chose an unscalable method precisely because it could bypass the defenses that protect against more widespread digital threats.
The Conference Itself as the Threat Model
The attendees of conferences, particularly those involving high-level executives from critical sectors like agriculture, represent prime targets. The inherent vulnerability lies in the period between the initial compromise and the detection of malicious activity – the runtime gap that begins only once the machine boots. The vendors showcasing their solutions at events like Fal.Con 2026 are, in essence, offering runtime protection to attendees whose own laptops harbor the same exploitable gap.
A significant impediment to effective defense against such sophisticated, multi-faceted attacks is organizational fracture. The responsibility for deploying Falcon Guardian, for instance, might fall under one team, while the crucial task of configuring BIOS settings on travel laptops rests with another. The Agentic Identity Provider might be managed by identity governance, while decisions about executives carrying production-access machines to international conferences might be made by a separate risk management group. Furthermore, the budget allocated for cloud threat defense is often entirely disconnected from the policies governing travel device security.
Meyers, having experienced security challenges from various perspectives, articulated this disconnect: "I’ve talked to companies where they’re like, we’re having a board meeting in Shanghai, and I’m like, why would you do that?" His implied question points to the inherent risks associated with conducting sensitive business in environments where physical security and digital security are not holistically addressed.
Essential Pre-Trip Security Measures for Leaders
Before embarking on their next international journey, security leaders must take proactive steps to close the exploitable gap that OVERCAST PANDA so effectively leveraged. For Windows laptops, the primary target of FlowCloud, the following audits and configurations are paramount:
- Audit USB Boot Status: The immediate priority is to verify that no device can be booted from USB without explicit authorization. If a laptop can be booted from USB out-of-the-box, it possesses the same vulnerability exploited this spring.
- Enforce Full-Disk Encryption with Pre-Boot Authentication: While BitLocker is a standard feature, relying solely on TPM-based encryption presents a documented weakness against physical access. As demonstrated by SCRT researchers in 2021, the volume master key can be extracted from the LPC bus with relatively inexpensive hardware. Similarly, the Dolos Group achieved the same over SPI. OVERCAST PANDA’s ability to write a backdoor and its post-boot trigger directly to the Windows volume suggests that either the machines were unencrypted or protected by a configuration that could be bypassed. Implementing pre-boot authentication with a PIN or USB key forces a human verification step before storage becomes accessible, significantly hardening the device.
- Verify Secure Boot and Revocation Lists: Secure Boot is designed to validate the authenticity of boot components, but it is not a panacea. Legacy Microsoft-signed UEFI shims, as highlighted by ESET research in July 2026, could still allow untrusted code to run at boot on machines that had not updated their revocation lists. Ensuring Secure Boot is enabled and the revocation list is current is vital. Furthermore, locking the boot order at the UEFI level, disabling one-time boot menus, and setting a strong BIOS administrator password that secures both the setup utility and any boot-override key are critical steps. The inconvenience of these measures often leads to them being overlooked.
- Issue Dedicated Travel Devices: For international conferences, organizations should provide executives with dedicated travel-only laptops. These devices should have no access to production systems, no saved credentials for internal tools, and no persistent VPN configurations, thereby limiting the potential damage of a compromise.
As Meyers succinctly put it, echoing an old DEF CON adage, "If they can get their hands on it, they can own it." The detection window for FlowCloud, and similar malware deployed via physical access, is the critical period between the USB write and the next login, a silent compromise that occurs while the laptop appears inert. The solution lies not in complex new technologies, but in the diligent implementation of established firmware settings and a pragmatic approach to device security. "It’s cheap to buy a couple of laptops and a couple of phones," Meyers concluded, emphasizing that the controls to close the exploit window are readily available, posing the question of whether organizations are willing to deploy them.
