 By admin
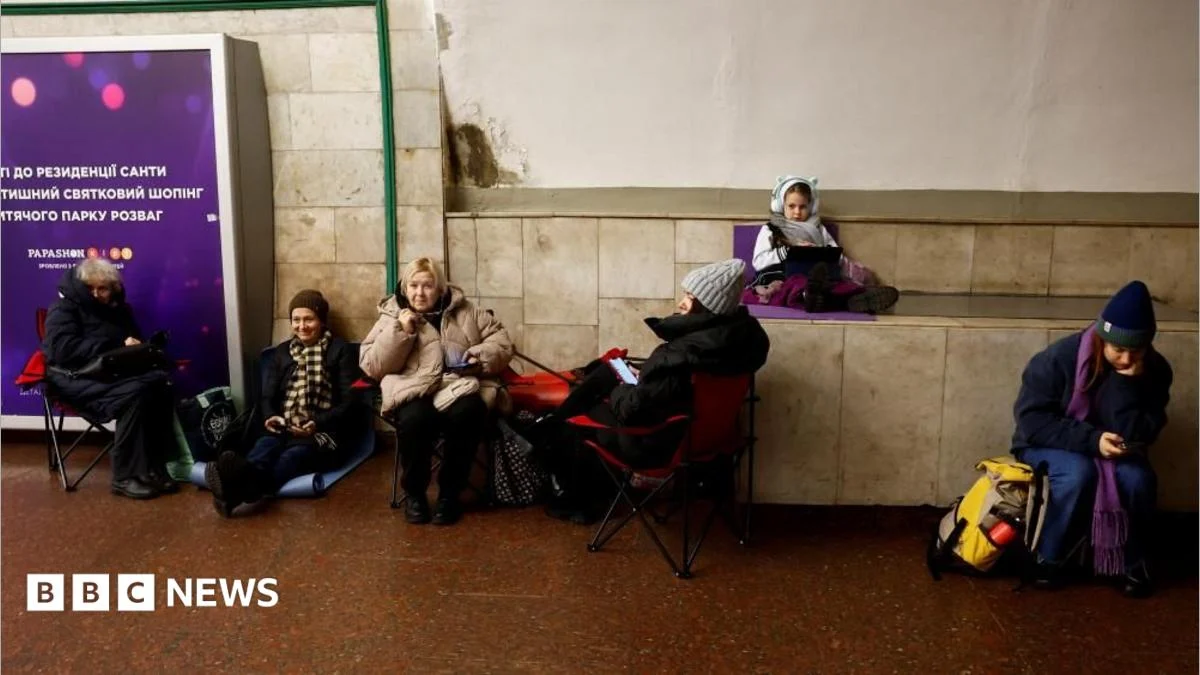
The apparent hacking incident, which unfolded on Sunday evening, saw Ukraine’s widely used "Air Alarm" application disseminate alarming and false messages about impending radiation and chemical threats in the capital, Kyiv. The Ukrainian Air Force, in a swift public statement via Telegram, addressed the widespread panic that ensued, assuring citizens that there was "no radiation threat" and urging them to remain calm and rely on official updates. The incident highlights the persistent vulnerabilities in digital infrastructure during times of conflict and the critical importance of maintaining secure and reliable communication channels for public safety.
The initial false alert, delivered in Ukrainian, began approximately at 22:47 local time (20:47 GMT). It ominously declared: "Radiation threat. Radiation threat declared in Kyiv." This message alone would have been enough to sow significant unease among a population already living under the constant shadow of war and the potential for escalated attacks. However, the situation quickly devolved into further confusion and alarm with subsequent messages.
A mere minute later, at 22:48, a second alert appeared, this time written in Russian. This message, while also alarming, contained a more cryptic and potentially dismissive tone, stating: "Hi! There will be a nuclear alert across Ukraine. Don’t worry, it’s Oreshnik flying." The reference to "Oreshnik" is particularly noteworthy. While not explicitly defined in the initial reports, it could be a coded term, a derogatory slang, or a deliberate attempt to mock or downplay the severity of the fabricated threat. The use of Russian further complicates the interpretation, potentially suggesting a specific actor or motive behind the hacking operation.
The disinformation campaign did not end there. At 22:49, a third alert, again in Ukrainian, escalated the fabricated threat, declaring: "Chemical threat. There is a threat of a chemical attack on Kyiv. Don’t go outside." This final message amplified the fear, introducing another terrifying dimension to the misinformation and reinforcing the imperative for citizens to seek shelter, thus potentially hindering their ability to verify information or access safer locations.
In response to the widespread panic and misinformation, the Ukrainian Central Intelligence Agency also issued a statement on Telegram. They confirmed that there had been a "failure in the app" and strongly urged the public to utilize "other sources of information to clarify the situation regarding the threat of air strikes." This admission of a "failure" could be interpreted in various ways – a technical malfunction, a deliberate sabotage, or a combination of both. The agency’s directive to seek alternative information sources underscores the critical need for a multi-pronged approach to emergency communication, especially when primary channels become compromised.
The incident raises several critical questions about the security of Ukraine’s digital infrastructure, particularly systems designed for public safety. The "Air Alarm" app is a vital tool for millions of Ukrainians, providing real-time updates on air raid sirens and missile threats. Its compromise, even for a short period, could have devastating consequences, leading to misdirected panic, unnecessary strain on emergency services, and potentially even loss of life if citizens are misled into dangerous actions or inaction.
The use of fabricated radiation and chemical threats is a tactic that weaponizes psychological warfare. In a country already grappling with the trauma of conventional warfare, the introduction of such existential threats, even if false, can have a profound and lasting impact on public mental health and societal resilience. The perpetrators, whether state-sponsored actors or independent groups, likely aimed to sow discord, erode trust in official communications, and exacerbate the already high levels of anxiety and fear within the Ukrainian population.
This incident is not an isolated event in the broader context of the ongoing conflict. Russia has a documented history of employing disinformation and cyber warfare as integral components of its military strategy. These tactics are designed to undermine an adversary’s morale, destabilize its society, and influence international perceptions. The use of sophisticated hacking techniques, coupled with the dissemination of fear-mongering messages, aligns with these broader objectives.
The "Oreshnik" reference, while obscure, could be a deliberate attempt to inject a sense of the absurd or a veiled threat. It’s possible that "Oreshnik" is a colloquial or slang term for a specific type of weapon or military operation, or it could be an attempt to make the alert sound less credible to some, while still causing panic among others. The inclusion of both Ukrainian and Russian messages suggests a targeted effort to reach different segments of the population and potentially to sow confusion about the origin and intent of the messages.
The reliance on a single application for critical safety alerts, while efficient in normal circumstances, exposes a potential single point of failure. Experts in cybersecurity and emergency management have long warned about the need for redundant and robust communication systems, especially in conflict zones. These systems should include a combination of mobile applications, traditional media broadcasts, public address systems, and community-based alert networks.
The fact that the hack occurred on a Sunday evening, a time when many would be seeking respite or spending time with family, might have been a deliberate choice to maximize the psychological impact. The rapid succession of alerts, each escalating the perceived threat, would have intensified the sense of urgency and helplessness.
The response from Ukrainian authorities, while swift, highlights the challenges of countering sophisticated cyberattacks in real-time. The Air Force’s immediate public statement and the Intelligence Agency’s confirmation of a "failure" were crucial steps in mitigating the damage. However, the underlying vulnerability that allowed the hack to occur needs to be thoroughly investigated and addressed.
This incident also underscores the importance of media literacy and critical thinking skills for the public. In an era of pervasive digital information, citizens are constantly bombarded with messages from various sources, some of which may be intentionally misleading. Developing the ability to discern credible information from disinformation is a crucial skill for navigating the complexities of modern conflict.
Further investigation into the technical aspects of the hack is essential. Understanding how the attackers gained access to the "Air Alarm" app, what vulnerabilities were exploited, and the extent of the compromise will be critical in preventing future incidents. This could involve analyzing server logs, reviewing application code, and potentially engaging international cybersecurity experts.
The psychological impact of such false alarms on a population already living under immense stress cannot be overstated. Repeated exposure to threats, even if later debunked, can lead to a phenomenon known as "threat fatigue," where individuals become desensitized to actual warnings, or conversely, to chronic anxiety and hypervigilance.
The long-term implications of this incident extend beyond immediate public safety. It could erode trust in the very systems designed to protect citizens, making it harder for authorities to disseminate critical information during future emergencies. It also provides valuable intelligence for adversaries seeking to understand and exploit Ukraine’s digital vulnerabilities.
In conclusion, the hacking of Ukraine’s "Air Alarm" app and the subsequent dissemination of false radiation and chemical threat alerts represent a concerning escalation in the use of cyber warfare and psychological operations. The incident serves as a stark reminder of the persistent threats to digital infrastructure, the critical importance of robust and redundant communication systems, and the need for heightened vigilance and critical thinking in an increasingly interconnected and volatile world. The Ukrainian authorities’ swift response and ongoing efforts to secure their digital assets are crucial, but the long-term battle against disinformation and cyber threats requires a multifaceted and sustained approach involving technological resilience, public education, and international cooperation. The psychological scars left by such deliberate misinformation campaigns can be deep and enduring, highlighting the human cost of these digital battles.
