 By admin
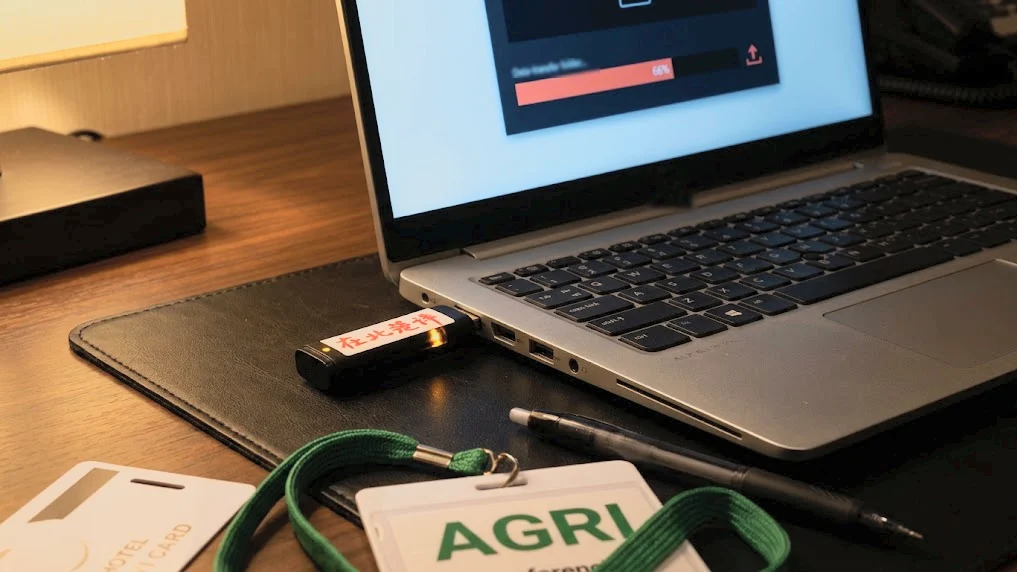
In a sophisticated and alarming operation, a Chinese state-linked hacking group, identified by cybersecurity firm CrowdStrike as OVERCAST PANDA, bypassed conventional digital defenses to compromise executive laptops at an agricultural industry conference on Hainan Island this spring. Instead of resorting to common tactics like phishing or network intrusions, the attackers employed a physical access strategy, gaining entry into hotel rooms and directly infecting unattended laptops with malware via USB drives while their owners were away. This audacious campaign, detailed in CrowdStrike’s 2026 Threat Hunting Report, highlights a concerning evolution in cyberattack methodologies, leveraging physical vulnerabilities that often fall outside the purview of traditional endpoint security solutions.
The timeline of the intrusions, as revealed in an interview with VentureBeat at Fal.Con 2026 by Adam Meyers, CrowdStrike’s senior vice president of counter adversary operations, paints a picture of meticulous planning and execution. The report indicates that intruders entered hotel rooms between March and May 2026, with specific timestamps showing an entry around 8 p.m. local time and a second room by 9:57 p.m. During these brief windows of opportunity, the attackers inserted a USB stick into each laptop, directly writing a sophisticated backdoor named FlowCloud to the machine’s storage. Crucially, the laptops were then immediately rebooted and left undisturbed, leaving no trace of network intrusion, phishing attempts, or stolen credentials. The compromise was complete at the firmware and operating system level before the executives returned.
FlowCloud, the malware employed in this campaign, is not a new threat. Proofpoint had previously documented its use in 2020, delivered via phishing to target the U.S. utilities sector. More recently, NTT Security’s Security Operations Center (SOC) has been tracking USB-delivered infections utilizing FlowCloud at overseas branches of Japanese organizations since early 2022. However, the OVERCAST PANDA campaign marks a significant escalation in its deployment. Security researchers have long recognized the concept of physically tampering with unattended laptops as an "evil maid attack," a term popularized by Joanna Rutkowska in 2009 when she demonstrated such an attack using a bootable USB stick. While physical access operations are relatively rare among the 290 named adversaries tracked by CrowdStrike, this incident stands out due to the direct involvement of a state intelligence service in executing the physical intrusion and malware deployment, bypassing user interaction altogether. Unlike other physical access methods, such as those employed by MUSTANG PANDA which rely on victims plugging in dropped USB drives, OVERCAST PANDA’s approach involved direct access to the target machine.
The impact of the attack became apparent the following morning when the executives powered on their laptops. Upon booting, the implanted FlowCloud backdoor was triggered, initiating a cascade of malicious activities including keylogging, screen capture, file collection, and credential harvesting. Meyers explained to VentureBeat that CrowdStrike’s visibility begins once the operating system loads and the Falcon sensor detects FlowCloud’s activity. The critical vulnerability exploited by OVERCAST PANDA was the silent window of compromise – the hours between the USB write and the subsequent boot, during which the laptop was infected and undetected.
This revelation comes at a significant time, as CrowdStrike concurrently announced its new slate of AI security products at Fal.Con 2026: Falcon Guardian, SafeMind, the Agentic Identity Provider, and AI Gateway. These advancements aim to address the evolving threat landscape, yet the OVERCAST PANDA incident underscores how sophisticated actors can operate below the detection thresholds of many contemporary security tools.
Why Existing Security Tools Missed the Mark
The effectiveness of the OVERCAST PANDA attack lies in its ability to circumvent standard security layers. Endpoint Detection and Response (EDR) solutions, for instance, typically require the operating system to be loaded and their agent to be running for effective monitoring. Multi-factor authentication (MFA) is designed to verify user identity during login attempts, and phishing training aims to educate users about malicious emails. AI agent security focuses on securing the agents themselves. OVERCAST PANDA’s "evil maid" tactic bypassed all these by completing the initial compromise at a level below the running operating system, below the EDR agent, and below the authentication stack. While CrowdStrike’s Falcon platform eventually detected FlowCloud once its process began after the boot, the implant and its trigger mechanism were already deeply embedded on the disk.
"Hotel entry is a very common thing," Meyers observed, highlighting that corporate physical security professionals are generally aware of such risks. "But I think what is unique is the combination of hotel entry with deployment of malware." He further posits that China’s Ministry of State Security (MSS) likely orchestrates OVERCAST PANDA, with the individuals entering the rooms being MSS or Ministry of Public Security officers, or potentially bribed or coerced hotel staff. The report also mentions a separate mid-2026 intrusion targeting a U.S.-based media professional using the same tradecraft, indicating a broader pattern of sophisticated espionage. The targeting of an agricultural conference is consistent with intelligence collection priorities tied to China’s national five-year plans, which often encompass advancements in food security and agricultural technology.
CrowdStrike’s Fal.Con Announcements and the Dawn of Runtime Security
The revelations from the OVERCAST PANDA campaign coincide with significant announcements at Fal.Con 2026. Nvidia CEO Jensen Huang joined CrowdStrike CEO George Kurtz on stage to unveil SafeMind, an agentic cybersecurity system built upon Nvidia’s Nemotron open models and CrowdStrike’s extensive threat intelligence. Meyers also highlighted the escalating vulnerability landscape, noting that 7,400 CVEs were registered in June 2026, a staggering 96% increase over June 2025. CrowdStrike itself was responsible for over 2,400 of these disclosures through responsible disclosure practices, underscoring the company’s active role in identifying and mitigating emerging threats.
Furthermore, Falcon Guardian, CrowdStrike’s runtime security solution for AI agents on the endpoint, was officially launched. CrowdStrike President Mike Sentonas announced its immediate availability. AI Gateway, a complementary capability, is slated for release as a hosted service in September, with a hybrid version to follow. AJ Shipley, CrowdStrike’s chief product officer, indicated that SafeMind models will be integrated into Guardian within weeks to enhance malicious-prompt detection.
The threats these new products aim to combat are demonstrably growing. CrowdStrike’s OverWatch team observed that AI agent-triggered detection leads increased at 2.5 times the rate of human-triggered leads. Cloud-conscious eCrime activity surged by an alarming 171% during the reporting period. Vishing (voice phishing) intrusions doubled in the first half of 2026 compared to the latter half of 2025, with the eCrime group SNARKY SPIDER demonstrating an ability to move from account takeover to data exfiltration in under five minutes after compromising SSO-integrated SaaS applications. While these threats are diverse, they universally rely on a running operating system, an active user session, or a live cloud workload – elements that the OVERCAST PANDA attack deliberately bypassed at the initial point of compromise.
Firmware and Policy: The Unsung Heroes of Defense
Meyers firmly stated that the "evil maid" attack is a "solvable problem," albeit one that requires "inconvenient solutions" that many organizations are reluctant to implement. CrowdStrike itself has been offering firmware attack detection and BIOS settings auditing capabilities through its Falcon sensor since May 2019, including integration with Dell SafeBIOS. This functionality, which allows for the auditing of security-related BIOS settings on enterprise laptops, has been available for seven years, suggesting that the gap exploited by OVERCAST PANDA was not a product deficiency but rather a failure in policy and implementation.
The controls that would have effectively thwarted the OVERCAST PANDA campaign are neither novel nor expensive. Disabling external boot in UEFI firmware is a fundamental step. A BIOS administrator password is essential to prevent unauthorized changes to these settings. Pre-boot authentication, requiring a PIN or USB key before the operating system loads, ensures that even if a foreign boot environment is introduced, the encrypted data remains inaccessible. Firmware monitoring can detect tampering after the fact.
Meyers’ stark advice to travelers is to "not bring anything with you that you’re not comfortable with handing over to a foreign intelligence service." He advocates for the use of temporary, disposable laptops and email accounts for overseas trips, with devices being wiped upon return. The risk, he warns, begins even before arrival, as customs officials can seize devices and compel logins. He also dismisses hotel safes as a viable security measure, stating, "They have master keys to that stuff."
Scale vs. Precision: The Shifting Landscape of Cyber Threats
While the OVERCAST PANDA hotel room operation is a prime example of a sophisticated, state-sponsored attack, CrowdStrike’s OverWatch team noted a plateau in overall intrusion growth, attributing it to a shift towards more complex and resource-intensive campaigns. When asked to compare the hotel room intrusion with a swift, AI-powered attack by the eCrime group REVENANT SPIDER, which compromised 17 victims with custom web shells in just 48 minutes, Meyers expressed greater concern for the latter.
"You can’t intrude on hotel rooms at scale," Meyers explained. "You can’t intrude on physical devices at scale. And even then, it’s just one device." Physical-access tradecraft, while highly effective against specific targets, is inherently limited by its manual nature and lack of scalability. In contrast, network-speed, AI-powered intrusions, like those demonstrated by REVENANT SPIDER, can affect thousands of machines simultaneously, making them a more significant concern for the average enterprise due to their sheer volume and speed. Security budgets, therefore, often prioritize threats that impact the largest number of systems. However, the OVERCAST PANDA incident serves as a potent reminder that targeted, low-volume attacks can achieve significant intelligence objectives precisely because they operate outside the typical threat models focused on scale.
The Conference as a Threat Model: Fragmented Security Efforts
The executives attending the agricultural conference were precisely the targets of a state intelligence service that deliberately chose an unscalable yet highly effective method to bypass digital defenses. At conferences, the laptops themselves become the primary attack surface, and runtime security, as exemplified by CrowdStrike’s new offerings, only becomes relevant once the machine boots. The irony is that the vendors exhibiting at Fal.Con 2026 were promoting runtime protection solutions to attendees whose own laptops likely shared the same fundamental vulnerability.
The core problem, Meyers suggests, is organizational fracture. Different teams are responsible for endpoint security, identity governance, and travel device policies. Falcon Guardian might be deployed by one team, while BIOS configuration for travel laptops falls under another. The budget for cloud threat defense may be entirely separate from the allocation for travel security protocols. This disconnect prevents a holistic approach to security, leaving critical gaps like the one exploited by OVERCAST PANDA. Meyers, drawing from his own experience, has witnessed companies planning board meetings in locations like Shanghai, a decision that immediately raises security red flags due to the inherent risks associated with conducting sensitive business in high-threat environments.
Pre-Trip Preparations: Securing Laptops Before the Next Journey
For security leaders and executives preparing for international travel, a thorough audit of every executive laptop is paramount. The immediate concern is whether the device can be booted from USB, a capability that represents the same critical gap exploited by OVERCAST PANDA. For Windows laptops, the primary target of FlowCloud, several key steps are essential:
-
Enforce Full-Disk Encryption with Pre-Boot Authentication: While BitLocker with TPM-only configuration offers some protection, it has been shown to be vulnerable to physical access attacks. Researchers have demonstrated methods to extract the volume master key from the LPC bus using inexpensive hardware modules. OVERCAST PANDA’s ability to write a backdoor directly to the Windows volume suggests that the targeted machines were either unencrypted or protected by a configuration that could be bypassed. Implementing pre-boot authentication with a PIN or a USB key introduces a necessary human step, rendering the storage unreadable until authorized access is granted.
-
Verify Secure Boot and Update Revocation Lists: Secure Boot is designed to validate the signatures of boot components, preventing unauthorized bootloaders. However, it can leave external media bootable, and legacy Microsoft-signed UEFI shims have been identified that allow untrusted code to run at boot. ESET research highlighted 11 such shims that undermined Secure Boot. Microsoft has since revoked these shims in its DBX updates. Laptops that have not received these updates remain vulnerable. Therefore, it is crucial to lock the boot order at the UEFI level, disable one-time boot menus, and enforce a BIOS administrator password that secures both the setup utility and any boot-override keys. These seemingly inconvenient configurations are vital for closing the physical access attack vector.
-
Issue Travel-Specific Devices: For international conferences and business trips, organizations should issue dedicated travel-only devices. These laptops should have no access to production systems, no saved credentials for internal tools, and no persistent VPN configurations. This minimizes the potential damage if the device is compromised.
"If they can get their hands on it, they can own it," Meyers reiterates, referencing an old DEF CON adage. The hours between the USB write and the next login, while the laptop sits closed and compromised, represent the critical window of exposure. The controls that can close this window are a handful of firmware settings and a dedicated travel laptop – solutions that are readily available and relatively inexpensive. The ultimate question remains whether organizations are willing to implement these fundamental security measures before their executives become the next targets of such sophisticated, unscalable, yet highly effective attacks.
